
 Do Son
A critical Fortra BoKS vulnerability (CVE-2026-9862) enables remote OS command injection via the autoregistration service. Mitigate now.
Fortra

A new 10.0 CVSS score vulnerability in Fortra's GoAnywhere MFT platform allows attackers to execute remote code. Learn how to protect your systems now.

Critical flaws in FileCatalyst Workflow pose a significant risk to sensitive data and systems. Learn about CVE-2024-6633 and CVE-2024-6632
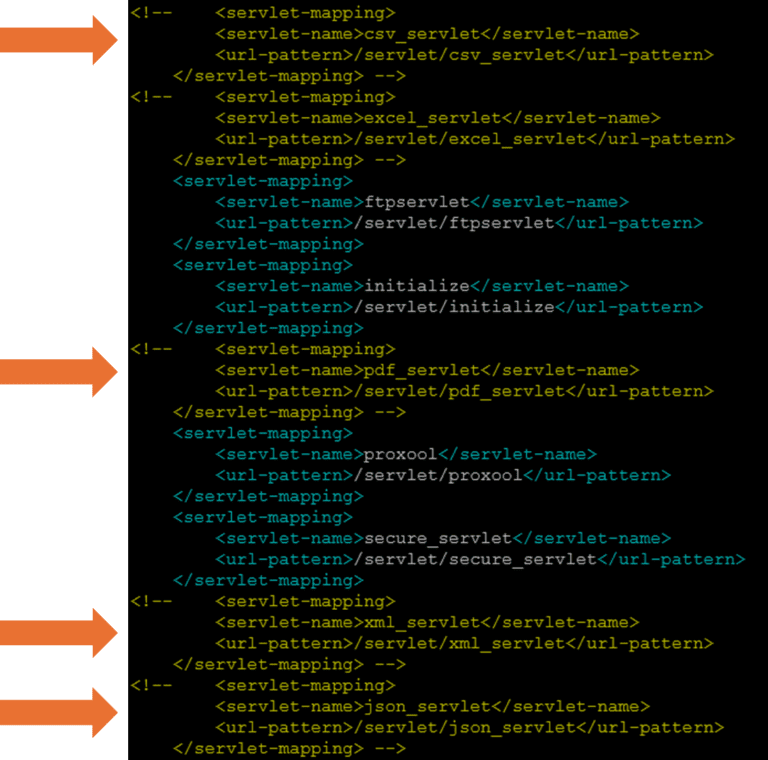
Tenable Research, who discovered and reported the CVE-2024-5276 flaw, has released a proof-of-concept (PoC) exploit code

Fortra has issued a security advisory warning users of a high-severity flaw (CVE-2024-5275) in both FileCatalyst Direct and FileCatalyst Workflow
Successful exploitation of the CVE-2024-4332 vulnerability could lead to unauthorized information disclosure or modification

CVE-2024-0259 allows low-privileged users to gain elevated privileges, potentially granting them full control over affected systems