 Do Son
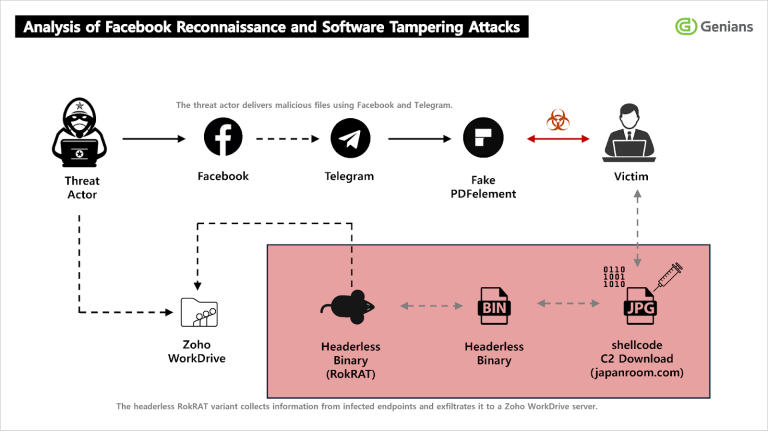
APT37 pivots to Facebook social engineering, using Wondershare PDFelement "code caves" to deploy RokRAT. Learn how they bypass EDR with memory-only payloads.
Genians Security Center
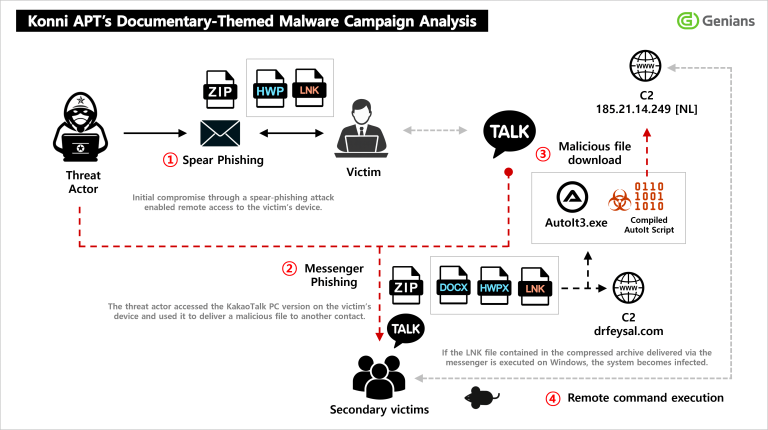
Genians Security Center reveals a new Konni APT campaign hijacking KakaoTalk PC sessions to distribute EndRAT, RftRAT, and RemcosRAT to trusted contacts.

Genians exposes APT37's Artemis campaign, where hackers pose as Korean TV writers using fake casting calls to deliver malware via HWP documents.

North Korean threat group Kimsuky is using AI-generated deepfakes in a new spear-phishing campaign, signaling a new frontier in cyber warfare.

North Korean APT Kimsuky is evolving its ClickFix tactics, using deceptive social engineering, fake job portals, and obfuscated PowerShell to compromise targets via spear-phishing campaigns.