 Do Son
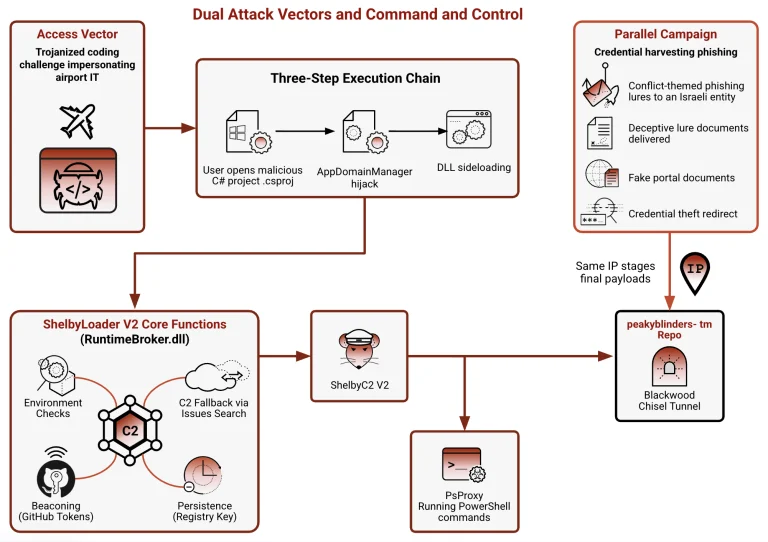
The Blinder Tunnel campaign used a fake Dubai Airports coding test to drop ShelbyLoader V2 on an Iraqi target. See how it works and how to defend.
Github C2
Zscaler details the C2Looper backdoor, a Rust backdoor tied to ransomware that uses GitHub for C2 and likely spreads through ClickFix lures.
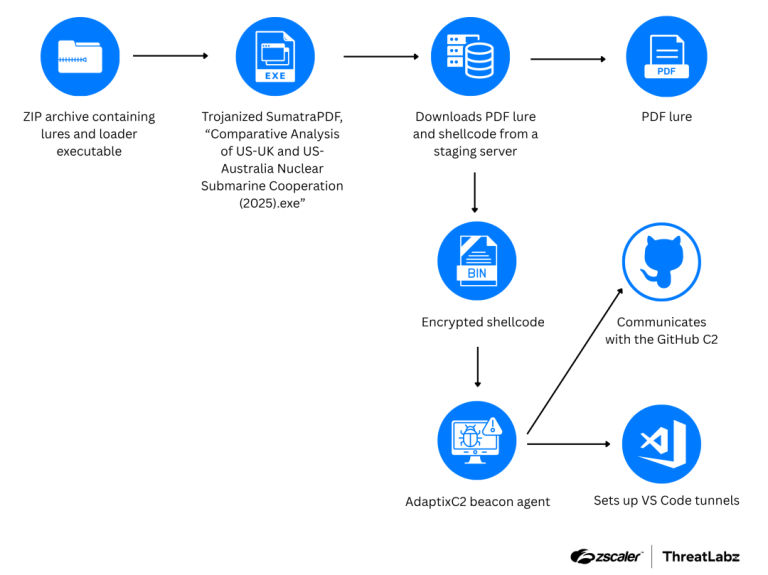
Tropic Trooper's 2026 campaign uses trojanized SumatraPDF and VS Code tunnels for stealthy East Asian espionage. Learn how to defend your infrastructure.
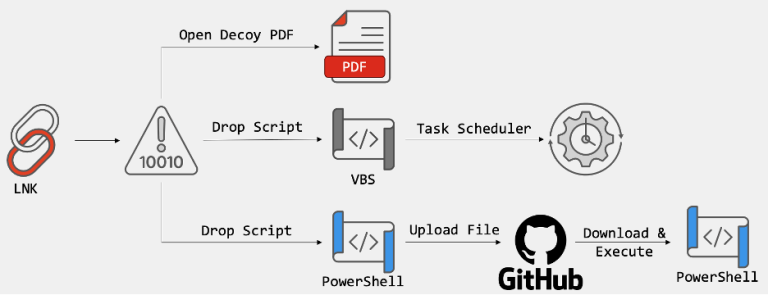
FortiGuard Labs unmasks a South Korean espionage wave abusing the GitHub API for C2 and using LNK files to stay invisible. Protect your network from LotL.

New "Gopher Strike" & "Sheet Attack" campaigns hit Indian govt. Linked to Pakistan, attackers use GitHub C2 & GenAI malware to evade detection.

JPCERT exposed APT-C-60 targeting Japan via VHDX LNK files in phishing emails. The SpyGlace malware uses GitHub to fetch encrypted commands and statcounter for victim telemetry.
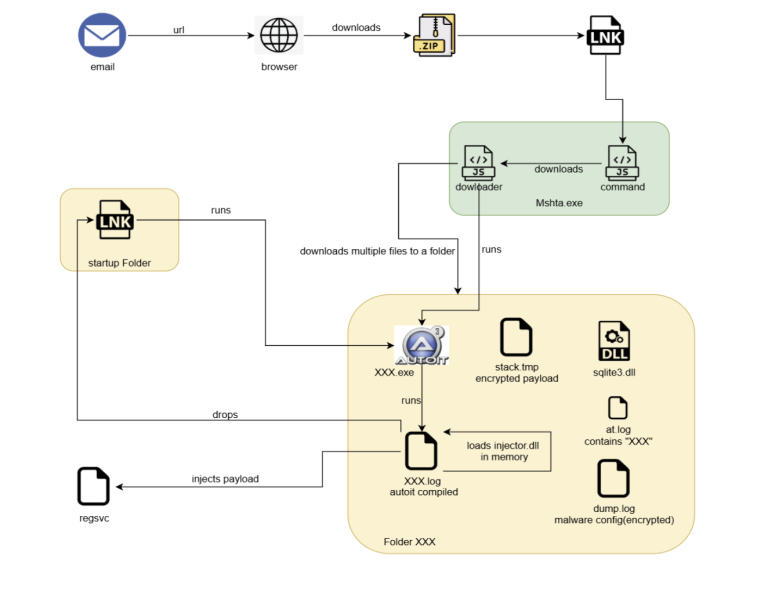
McAfee uncovered the Astaroth banking Trojan using GitHub for C2 backup, hiding encrypted configuration data via steganography in images to target Brazilian financial and crypto users.

The FlowerPower campaign ingeniously masquerades as interview requests from foreign news channels, leveraging the widely used Korean HWP