
 Do Son
Weeks after a major takedown, Lumma Stealer has resurfaced with new stealth tactics, exploiting cracked software, fake CAPTCHAs, and GitHub to resume its credential-stealing operations.
github

GitHub now allows users to sign in and create new accounts using their Google credentials, offering a streamlined login experience for developers.

Cisco Talos uncovers a sophisticated MaaS operation leveraging public GitHub repos and the Emmenhtal loader to distribute Amadey, SmokeLoader, and AsyncRAT, often via phishing.

A malicious campaign on GitHub is distributing Lumma Stealer via fake "Free VPN for PC" and "Minecraft Skin Changer" repositories, using obfuscation and process injection for stealthy delivery.

ReversingLabs exposes a supply chain compromise of the VS Code ETHcode extension via two lines of malicious code in a GitHub PR, leading to malware deployment.
North Korean APT Kimsuky is using GitHub private repos, Dropbox, and XenoRAT malware via spearphishing to compromise victims and conduct cyber-espionage.

Banana Squad has compromised over 60 GitHub repos with malicious Python files, using UI quirks to hide malware and steal data from developers via a sophisticated supply chain attack.

A new campaign, "Stargazers Ghost Network," weaponizes Minecraft mods on GitHub to distribute a multi-stage infostealer, targeting user credentials and crypto wallets.

Water Curse is using GitHub to distribute malicious open-source projects, weaponizing 76 accounts with multi-stage malware targeting developers, red teamers, and gamers.

OpenAI Codex now generates multiple code solutions per task, with enhanced monitoring, task cancellation, and improved handling of network restrictions for developers.

CYFIRMA uncovers DuplexSpy, a powerful C# RAT on GitHub with surveillance, persistence, and anti-analysis features, posing a significant cybercrime threat.

Google proposes restricting websites from accessing local network devices without explicit user permission. This enhances privacy and user control over web access.

Sophos X-Ops found a backdoored Sakura RAT targeting hackers and cheaters, spreading info-stealers via hidden scripts in open-source projects.

Microsoft's "Edit" command-line text editor is set to be pre-installed in Windows 11, offering simple text file manipulation.

A study reveals widespread path traversal (CWE-22) in open-source projects, exacerbated by LLMs generating insecure code. Automated detection and patching are critical.

A critical GitHub MCP server vulnerability allows AI agent hijacking via prompt injection, leading to data exfiltration from private repositories.

North Korean threat group Slow Pisces targets crypto developers with fake job offers and malicious coding challenges. Learn how they steal millions

Uncover the details of the Lazarus Group malicious campaign targeting the npm ecosystem with advanced malware techniques.
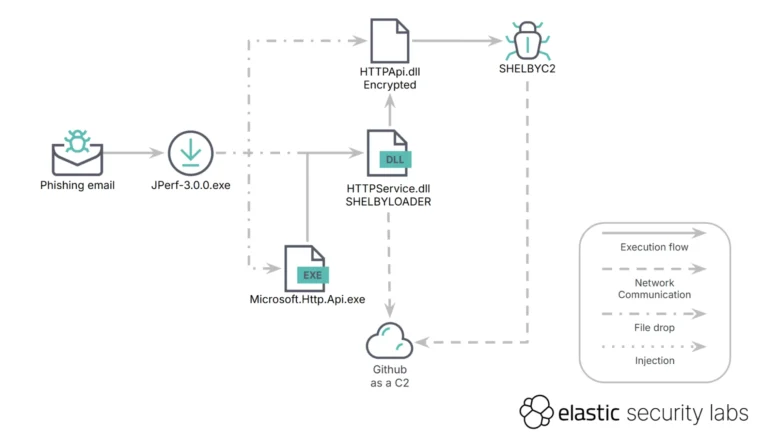
Uncover the SHELBY Malware, a sophisticated threat using GitHub for command-and-control in targeted enterprise attacks.

Explore the evolving threat of Albabat ransomware targeting Windows, Linux, and macOS systems with new, undetected variants.

Learn how SmartLoader is being spread through deceptive GitHub repositories, targeting users with gaming and software tools.

Explore how the Blind Eagle group has evolved since 2018, employing advanced tactics like Remote Access Trojans to conduct cyber espionage.