Skip to content
November 12, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Technology
  • GitHub Now Supports Google Social Login: Streamlined Sign-in for Developers
  • Technology

GitHub Now Supports Google Social Login: Streamlined Sign-in for Developers

Do Son July 22, 2025 2 minutes read
0
GitHub Social Login, Google Integration

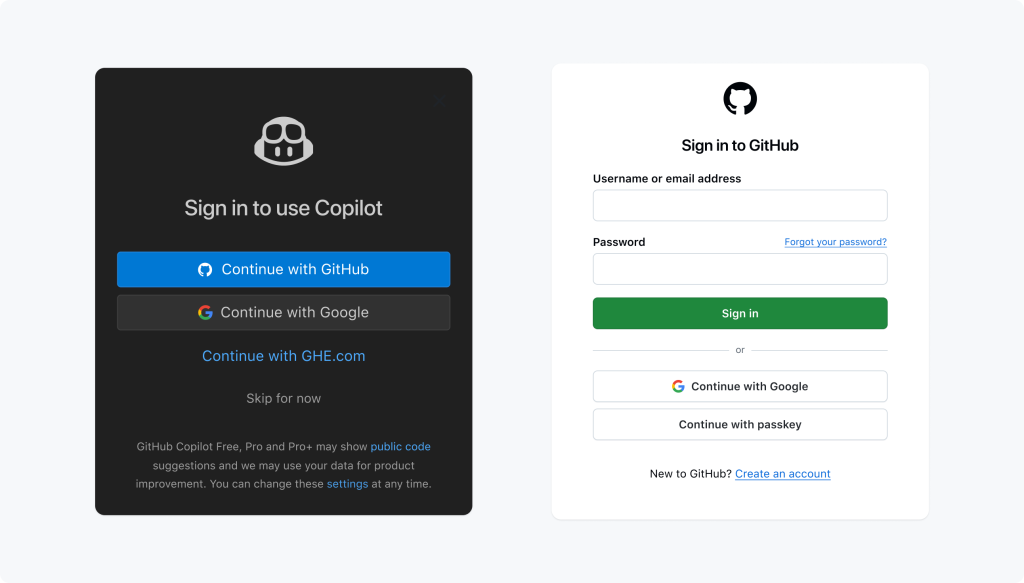
The code hosting platform GitHub recently announced via a blog post that it has introduced social login options, with Google accounts being the first to receive support. This means users can now sign in to GitHub directly using their Google credentials and create a new account linked to their Google-associated email address.

When registering through Google, the platform defaults to the email tied to the Google account and does not generate a password, as future logins can be handled seamlessly through Google authentication. As a result, users can continue using their Google account without ever setting a password.

However, it is strongly recommended that after signing in with a Google account, users manually verify their email and set a password within GitHub’s account settings. This precaution ensures continued access to the GitHub account should the associated Google account ever become suspended or inaccessible.

Can existing GitHub accounts be linked to Google for faster login? For now, the answer is no. GitHub’s blog post does not mention such functionality, and an examination by BlueDot Network of the account settings revealed no available option to associate existing accounts with Google.

Additionally, GitHub noted that Google login is also supported within the Visual Studio Code integration, allowing users exploring GitHub Copilot to register effortlessly and begin experimenting with AI-assisted coding.

It is anticipated that GitHub will expand support to other social login providers in the future, such as Microsoft, Facebook, and Apple—offering users a frictionless and convenient way to register or sign in to GitHub through widely used platforms.

Related Posts:

  • Hackers are selling legal Code Signing Certificates
  • GitHub Security Alerts has detected over 4 million vulnerabilities
  • Microsoft Signals End of an Era: Control Panel to be Phased Out
  • The Escalating Threat of the EV Code Signing Certificate Black Market
Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Microsoft Edge Google Account Login Coming Soon
  • Pentest-Tools.com Review: Your All-in-One Platform for Streamlined Penetration Testing and Vulnerability Management
  • Nitori Data Breach Exposes 37.6 Million Customer Records
  • Classic Outlook Interface Update Refines Windows Experience
  • Google Antigravity Knowledge Work Interface Launches
  • worse_query iOS Sandbox Escape Exposes Crypto Wallets
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: authentication Convenience Developer Tools github Google Account Sign-in Social Login Tech News

Leave a Reply Cancel reply

You must be logged in to post a comment.

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-126785CVSS 9.3
    A vulnerability has been found in rmalright TR-VISION HOME 2.0.5. Impacted is the function sub_11504 in the library...
    📅 Updated: Nov 12, 2026
  • CVE-2022-23851CVSS 9.8
    Netaxis API Orchestrator (APIO) before 0.19.3 allows server side template injection (SSTI).
    📅 Updated: Nov 11, 2026
  • CVE-2026-30530CVSS 9.8
    A SQL Injection vulnerability exists in SourceCodester Online Food Ordering System v1.0 in the Actions.php file (specifically the...
    📅 Updated: Nov 11, 2026
  • CVE-2026-34873CVSS 9.1
    An issue was discovered in Mbed TLS 3.5.0 through 4.0.0. Client impersonation can occur while resuming a TLS...
    📅 Updated: Nov 11, 2026
  • CVE-2026-36235CVSS 9.8
    A SQL injection vulnerability was found in the scheduleSubList.php file of itsourcecode Online Student Enrollment System v1.0. The...
    📅 Updated: Nov 11, 2026
  • CVE-2026-40575CVSS 9.1
    OAuth2 Proxy is a reverse proxy that provides authentication using OAuth2 providers. Versions 7.5.0 through 7.15.1 may trust...
    📅 Updated: Nov 11, 2026
  • CVE-2026-30269CVSS 9.9
    Improper access control in Doorman v0.1.0 and v1.0.2 allows any authenticated user to update their own account role...
    📅 Updated: Nov 11, 2026
  • CVE-2026-32604CVSS 9.9
    Spinnaker is an open source, multi-cloud continuous delivery platform. In versions prior to 2026.1.0, 2026.0.1, 2025.4.2, and 2025.3.2,...
    📅 Updated: Nov 11, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.