
 Do Son
Wiz Research reveals CVE-2026-3854, a critical GitHub RCE. One git push could expose millions of repos. GHES users must patch to v3.19.3 immediately.
github
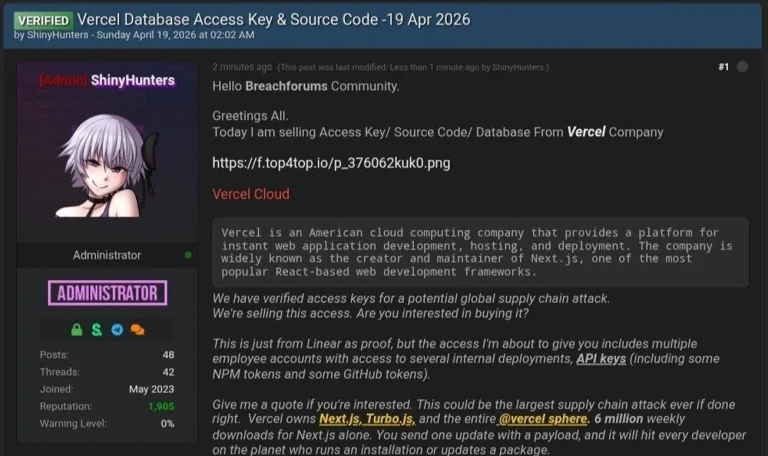
Vercel investigates a major breach by ShinyHunters. With Next.js source code and tokens at risk, developers must rotate secrets immediately. Stay updated.
PolinRider targets 1,900+ GitHub repos using "history-falsification" to hide malware. DPRK's Lazarus Group uses fake job tests to breach developers.

GitHub has suspended all Copilot Pro trials as of April 13, 2026. Learn how bad-faith exploitation forced a service-wide shutdown and what it means for you.

North Korea’s "graphalgo" campaign uses fake job interviews and real Florida LLCs to infect developers. Learn how to spot this sophisticated state-sponsored trap.
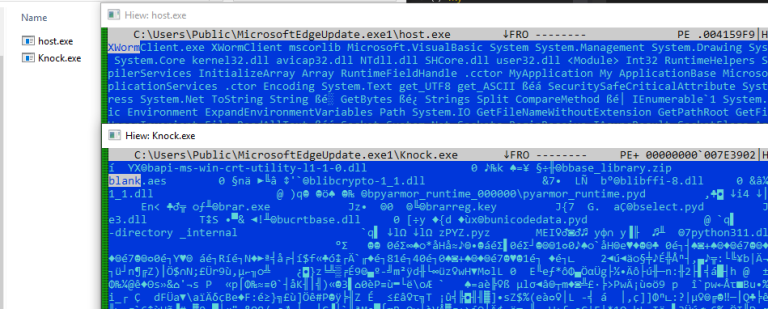
Splunk unmasks BlankGrabber: a modular Python info stealer using Discord and GitHub to swipe credentials and Discord tokens. Learn how to stay protected.

Anthropic's 8,100-repo DMCA sweep for Claude Code accidentally nuked thousands of legitimate forks. Discover the fallout and the silent restoration on GitHub.

Anthropic strikes back after the Claude Code leak, nuking 8,100 GitHub repos. But can you ever truly delete the internet's most wanted source code?

GitHub Copilot was caught secretly injecting ads for Raycast and Microsoft Teams into 11,000+ PRs. See how they hid the code and why developers are furious.

Netskope uncovers TroyDen’s Lure Factory, an AI-powered operation using 300+ trojanized GitHub repos and a 29,000-year sleep to steal credentials.

Starting April 24, 2026, GitHub Copilot will use your code to train its AI by default. Learn how to protect your intellectual property and opt-out today.

Clément Labro releases a public PoC for CVE-2026-20817, a critical Windows LPE flaw in the WER service. Patch now to prevent SYSTEM-level hijacking.

Jamf Threat Labs uncovers GhostClaw, a macOS threat exploiting GitHub stars and AI workflows to steal credentials. Protect your dev environment today!

Full disclosure: Technical details and a GitHub PoC for CVE-2025-39946 are live. This Linux TLS vulnerability allows root escalation via memory shaping.

Tech giants pledge $12.5M to help open-source maintainers survive a "tempest" of AI-generated bug reports. Discover the 2026 plan to fortify the global supply chain.

Frustrated by GitHub outages, OpenAI is reportedly building its own "agent-first" code-hosting platform. Is this the end of the Microsoft-OpenAI partnership?
Microsoft Build 2026 moves to San Francisco on June 2–3. With a 2,500-attendee limit at Fort Mason, the focus is on "Agentic AI" and deep technical immersion.

OpenAI hires OpenClaw creator Peter Steinberger to lead its "Personal Agent" revolution, aiming to turn ChatGPT into a proactive, task-executing concierge.

Clawdbot is the viral "Local-First" AI agent turning Mac minis into personal digital employees. See why GitHub's latest star is a must-have for 2026.
Attackers exploit GitHub forks ("Repo Squatting") to push HijackLoader malware via official-looking URLs. Technique remains active; verify all downloads.

Wiz reveals "CodeBreach": A regex typo in AWS CodeBuild could have let hackers hijack the AWS Console via the JS SDK. Issue is now patched.

Elon Musk vows to open-source X’s recommendation code and ad algorithms by mid-Jan 2026, targeting full transparency amid intense EU regulatory pressure.