
 Do Son
Synology patches a critical 9.8 CVSS Telnet flaw (CVE-2026-32746). Unauthenticated attackers can hijack your NAS. Update DSM or disable Telnet now!
GNU Inetutils
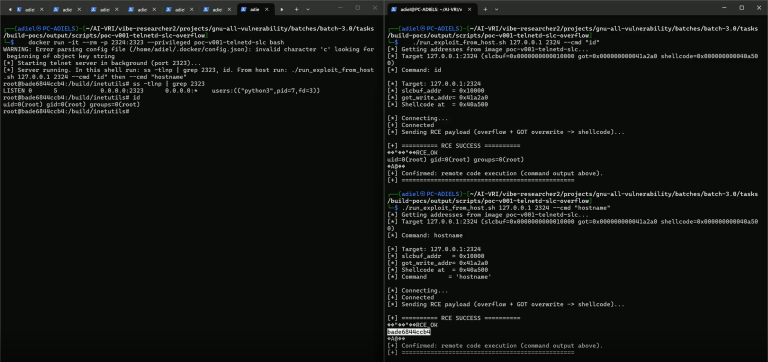
A critical 9.8 CVSS pre-auth buffer overflow in GNU Inetutils telnetd allows attackers to execute arbitrary code and gain root access. Patch immediately.
On January 29, 2026, Synology, a preeminent manufacturer of Network Attached Storage (NAS) solutions, disseminated a series...

Critical GNU Inetutils telnetd flaw allows unauthenticated root access via "-f root". Affects v1.9.3-2.7. Disable telnet immediately to stay safe.