 Do Son
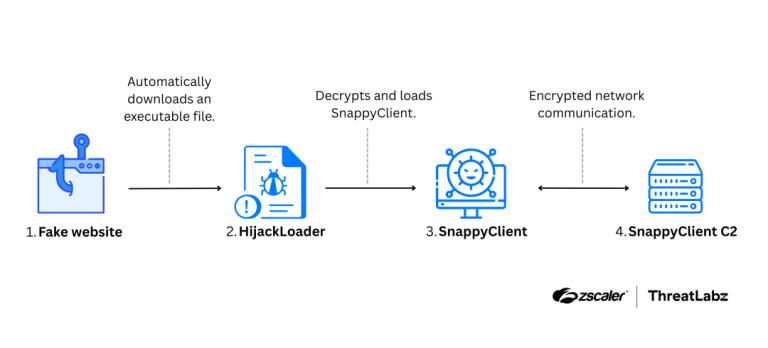
Zscaler ThreatLabz unmasks SnappyClient, a C++ C2 framework linked to HijackLoader. It uses AMSI bypass and Heaven’s Gate to steal crypto and gain remote access.
Heaven’s Gate

AmateraStealer (formerly ACRStealer) has significantly evolved, using low-level NTAPIs, Heaven's Gate, and multi-layered encryption to evade detection and steal sensitive data.

CVE-2025-31324 lets attackers exploit SAP NetWeaver to upload webshells and deploy C2 tools like Brute Ratel, affecting patched enterprise systems.

Trellix analysis reveals Lumma Stealer's latest tactics: code obfuscation, API hashing, ETW evasion, anti-VM. Learn how this InfoStealer avoids detection.

As the tax season rolls in, so does the threat of cybercrime, and leading the charge in 2024 is the infamous TA576 threat actor