 Do Son
Node.js fixes 17 bugs, including Node.js HTTP/2 vulnerabilities and a TLS heap leak (CVE-2026-123864). Update to 26.13.1, 24.22.3 or 22.23.5.
HTTP/2
Eight Apache Tomcat vulnerabilities, including a JNDIRealm authentication bypass, are fixed in 11.0.27, 10.1.61 and 9.0.123. Upgrade now.
The cURL CVE-2026-92392 vulnerability enables remote code execution during HTTP/2 uploads. Update to cURL 8.23.0 or disable HTTP/2 to protect systems.

Node.js patched 11 vulnerabilities in its July 2026 release. The high-severity bugs include a HTTP/2 use-after-free (CVE-2026-56848). Update now.

Apache releases v2.4.67 to fix an HTTP/2 Double Free RCE (CVE-2026-23918) and auth bypasses. Millions of servers are affected—upgrade your infrastructure now!
Node.js releases critical updates for 20.x to 25.x, fixing high-severity flaws like the __proto__ header crash and TLS errors. Update to v25.8.2 now.
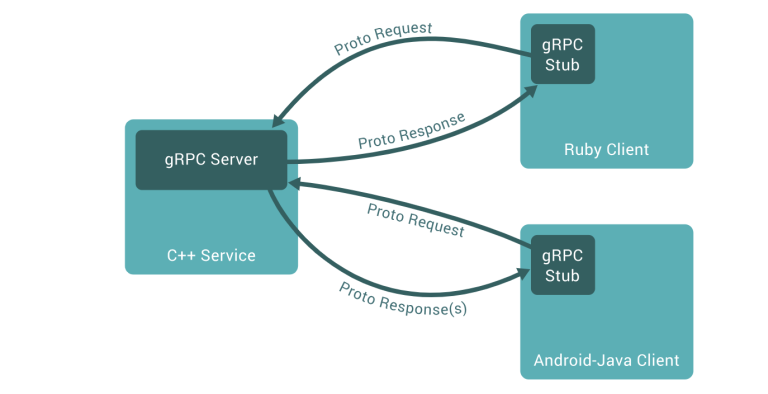
A critical 9.1 CVSS flaw in gRPC-Go (CVE-2026-33186) allows attackers to bypass authorization by omitting a leading slash. Upgrade to v1.79.3 immediately.

Microsoft released an emergency update for Windows 11 (24H2/25H2) to fix the critical bug that broke localhost/127.0.0.1 authentication for developers.

A new vulnerability, "MadeYouReset," has been discovered in HTTP/2, allowing attackers to exploit stream resets to launch devastating denial-of-service attacks.

Apache Tomcat 9.0.107 patches three critical DoS flaws (CVE-2025-52434, CVE-2025-52520, CVE-2025-53506) that can disrupt web services via HTTP/2, file uploads, and excessive streams.

New CrossPUSH & CrossSXG attacks exploit HTTP/2 and SXG to bypass Same-Origin Policy, enabling XSS and cookie manipulation.