 Do Son
An Amazon ClickFix campaign uses a fake CAPTCHA and the old Windows finger command to drop Lumma Stealer and NetSupport. Stay protected.
Huntress
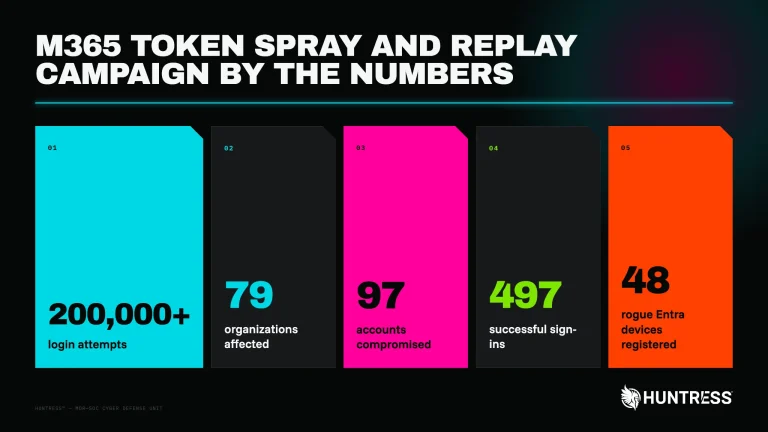
A token replay attack hit 79 organizations, bypassing MFA to set up Microsoft 365 BEC with rogue devices and hidden inbox rules.
Hackers abused a SkyKick API secret in a ConnectWise Cloud Backup breach, accessing 300+ Microsoft 365 tenants and planting rogue app credentials.
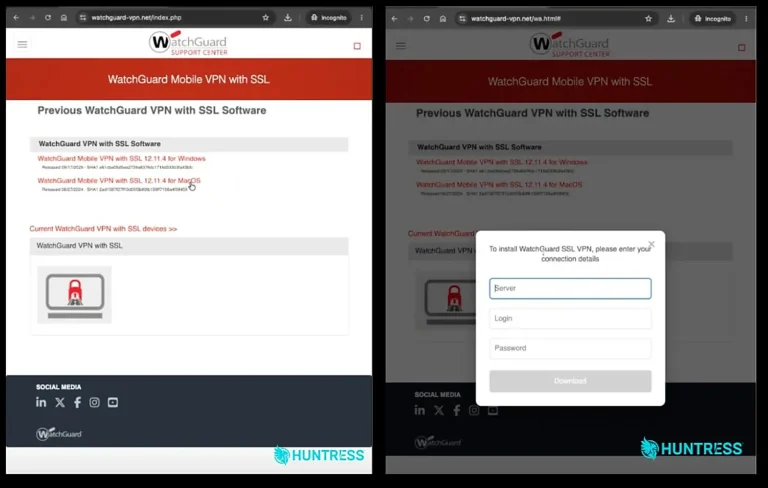
Huntress uncovers a WatchGuard VPN phishing campaign where a WatchGuard VPN phishing site steals logins twice before serving the real client.
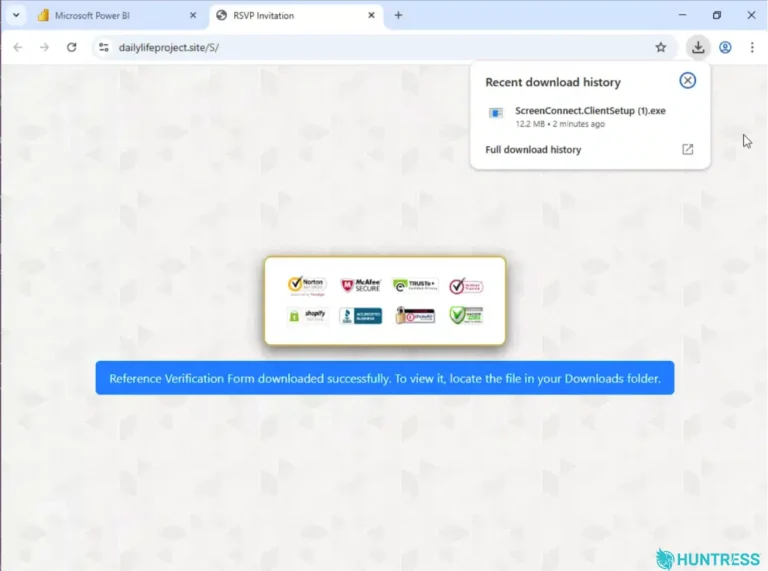
A Power BI phishing campaign uses Microsoft's real domain to install rogue ScreenConnect clients. Learn how it works and how to block it.
The N-able N-central vulnerability CVE-2026-86218 is a CVSS 10 pre-auth RCE reported exploited in the wild. Apply 2026.3 HF4 immediately.

Huntress exposes "VSOCKpuppet" VM escape: Attackers used a hidden zero-day toolkit to breach VMware ESXi hosts and bypass network monitoring.

Huntress exposed a covert campaign using log poisoning on exposed phpMyAdmin to deploy a web shell and the Nezha monitoring tool, ultimately delivering the Ghost RAT backdoor to 100+ victims in Asia.

Huntress details a multi-stage attack that uses DLL sideloading and obfuscated Python to deliver PureRAT, a commercial-grade remote access trojan linked to PXA Stealer.

A new Go-based ransomware, Obscura, is abusing domain controllers by placing its executable in the NETLOGON folder, ensuring it gets replicated across the network.

A new report from Huntress reveals a hybrid ClickFix attack that abuses the Windows search protocol and malicious LNK files to deliver MetaStealer malware.

A new ransomware strain called Cephalus is using compromised RDP, DLL sideloading, and abused security tools to bypass defenses and intimidate victims.

Huntress and other firms warn of a likely zero-day vulnerability in SonicWall VPNs. Attackers are bypassing MFA and deploying Akira ransomware within hours of initial access.

CISA adds critical Wing FTP Server RCE flaw (CVE-2025-47812, CVSS 10.0) to KEV. Actively exploited via null byte and Lua code injection; patch to 7.4.4 immediately!

Huntress witnessed active exploitation of a critical RCE flaw (CVE-2025-47812) in Wing FTP Server, allowing root/SYSTEM access via null byte injection and Lua code execution.

North Korean APT BlueNoroff (TA444) exploited deepfakes in Zoom calls to trick a crypto foundation employee into installing custom macOS malware for digital asset theft.