 Do Son
Four OpenAM vulnerabilities are fixed in 16.1.2. CVE-2026-62379 (CVSS 9.8) allows unauthenticated remote code execution; CVE-2026-62261 scores 9.9.
IAM

Urgent: Fortinet warns of 9.1 severity flaws in FortiSandbox (CVE-2026-26083) and FortiAuthenticator (CVE-2026-44277). Patch now to prevent unauthorized RCE.

Trend Research warns that ransomware is shifting to AWS S3, exploiting misconfigured IAM and SSE-C keys in five attack variants to cause irreversible data loss and cloud-native extortion.
Rapid7 identified the Crimson Collective using TruffleHog to find leaked AWS IAM keys. The group achieves Admin access to steal data from RDS/S3 and extort victims.
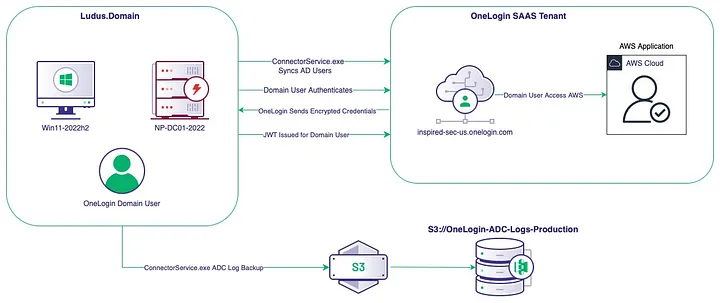
A critical flaw in OneLogin's AD Connector exposed API keys, allowing attackers to impersonate users across organizations via unclaimed S3 buckets and forged JWT tokens.

Learn about a massive ransomware campaign targeting over 100,000 domains. Understand the user errors in cloud services that enabled the attack and the impact on data security.