 Do Son
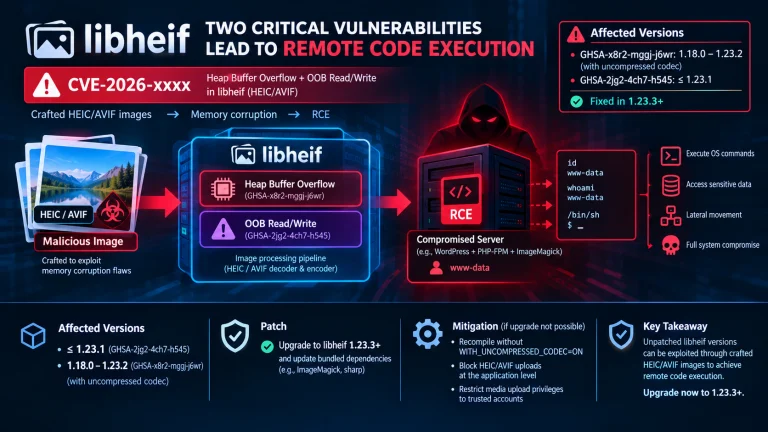
Details and PoC exploit code are out for critical libheif vulnerabilities GHSA-x8r2-mggj-j6wr and GHSA-2jg2-4ch7-h545. Upgrade to 1.23.3 now.
ImageMagick
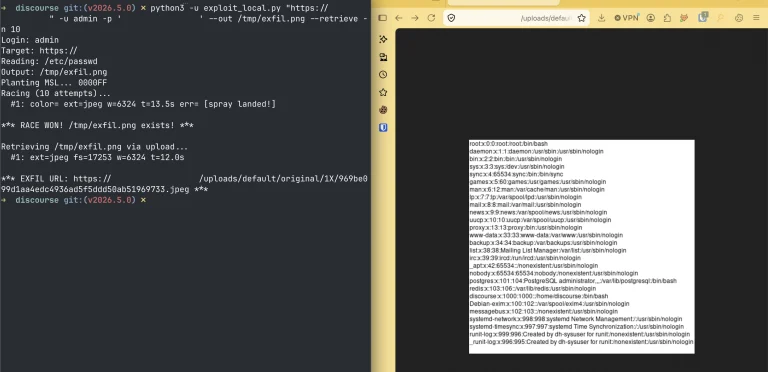
Two Discourse vulnerabilities, CVE-2026-55674 and CVE-2026-55420, enable cache poisoning XSS and server file reads. Patch to the fixed releases now.
A critical Ghostscript vulnerability, CVE-2026-39919 (CVSS 9.8), allows remote code execution via crafted PDFs. Update Ghostscript to 10.08.0 now.
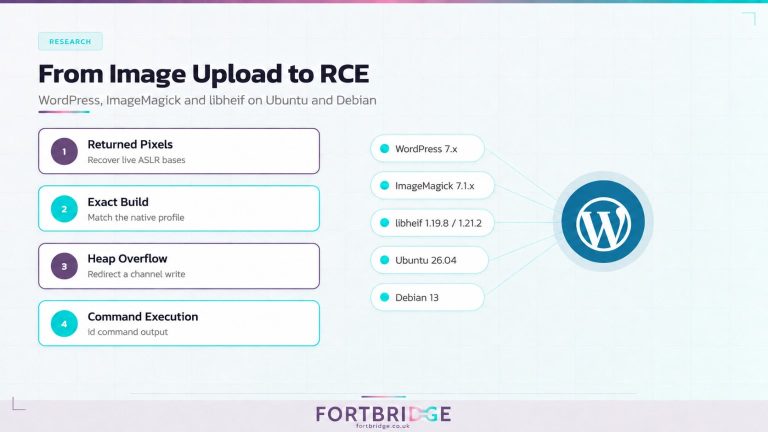
A WordPress libheif RCE chain and its PoC are now public. The libheif vulnerability turns an HEIC upload into code execution. Patch to 1.23.3.
High-severity ImageMagick flaw CVE-2026-23876 allows heap buffer overflows via XBM images. Update to v7.1.2-13 to prevent remote attacks.
A High-severity (CVSS 7.5) flaw in ImageMagick's PSX TIM parser allows Arbitrary Memory Disclosure on 32-bit systems via an integer overflow. Patch immediately to v7.1.2-10.

A critical vulnerability (CVE-2025-57807) was found in ImageMagick's blob subsystem, allowing attackers to corrupt memory and potentially execute arbitrary code.
A critical vulnerability in ImageMagick's BMP encoder (CVE-2025-57803) could allow remote code execution. Update your 32-bit builds immediately.

ImageMagick has a format string bug (CVE-2025-55298) that can lead to RCE. A PoC is public, and an urgent patch is available for versions 7.1.2-2 and 6.9.13-28.
ImageMagick has patched four security vulnerabilities, including high-severity memory corruption bugs, that could affect applications using the toolkit.

A critical command injection flaw (CVE-2025-54418, CVSS 9.8) in CodeIgniter's ImageMagick handler allows remote code execution via malicious filenames or text.

A flaw (CVE-2025-53101) in ImageMagick allows stack buffer overflows via filename templates, risking memory corruption and remote code execution. Patch now!

Urgent warning from CISA: Actively exploited vulnerabilities in ImageMagick, Linux Kernel, and SonicWall. Learn how to safeguard against potential cyberattacks.

Protect your systems from the ImageMagick vulnerability. Learn about the security flaw that could lead to data breaches and system compromise.
CVE-2023-34152 is an ominous manifestation of remote code execution (RCE) vulnerability in OpenBlob when configured with --enable-pipes