 Do Son
Learn how the LLM-generated PhantomRaven information stealer targets developers. The PhantomRaven information stealer uses npm to hijack CI/CD secrets.
information stealer
Veil#Drop malware abuses Blogspot to run PowerShell loaders and deploy PureLog Stealer in memory, dodging antivirus and file-based detection.
CVE-2026-48558, a SimpleHelp authentication bypass, is exploited in the wild to deploy TaskWeaver and Djinn Stealer. CISA added it to KEV. Patch now.

The SolyxImmortal info stealer targets user data. Learn how this Python malware steals passwords and abuses Discord webhooks to exfiltrate files.

ThreatLabz unmasks Xloader 8.7, the evolved successor to Formbook. Learn how its advanced obfuscation and decoy C2s bypass modern security defenses.

SantaStealer, a new MaaS info-stealer, is being aggressively marketed on the dark web. It's a BluelineStealer rebrand that uses C code and open-source libraries to steal crypto wallets and credentials, despite having amateur anti-analysis features.

Operation MoneyMount-ISO targets Russian financial institutions with a Phantom Stealer info-stealer hidden in an ISO file. The malware steals crypto wallets, browser data, and uses a keylogger. It has a SelfDestruct function for evasion.

A Lumma Stealer campaign is using fake update lures on Itch.io. The malware uses a Node.js-compiled executable and a reflective loading technique to steal passwords and crypto wallets.

Operation Hanoi Thief targets Vietnam with a pseudo-polyglot LNK/image file that executes malicious code via ftp.exe. The attack deploys LOTUSHARVEST stealer via DLL sideloading to steal Chrome/Edge credentials.

CYFIRMA uncovers XillenStealer, a new Python-based, open-source malware on GitHub. Its built-in builder enables even novices to steal data and credentials.
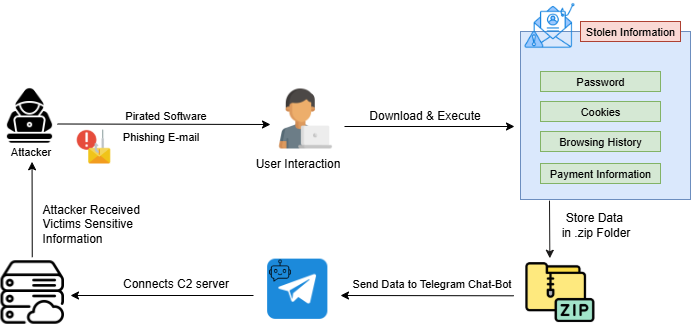
A new malware called Raven Stealer is emerging, targeting individuals and businesses by stealing credentials and data, and exfiltrating it via Telegram.

A new report reveals a dangerous malware campaign on a popular game piracy site, proving that even with an adblocker, pirated software is a huge risk.

A new report from Cisco Talos details PS1Bot, a modular PowerShell-based malware campaign using malvertising to steal data and maintain stealthy persistence.
A hacker is allegedly selling 16 billion login credentials, likely aggregated from past breaches via info-stealing malware, impacting major tech platforms. Use MFA to stay safe!

HelloTDS is a sophisticated traffic direction system delivering millions to FakeCaptcha and other malware via advanced fingerprinting and evasive tactics.

Interpol and Asian law enforcement blocked 20,000 malicious IPs and seized 41 servers in a major takedown of information-stealing malware infrastructure.

A sophisticated "ClickFix" phishing campaign uses fake Booking.com CAPTCHAs to deliver RATs and info stealers to the hotel and travel industry.
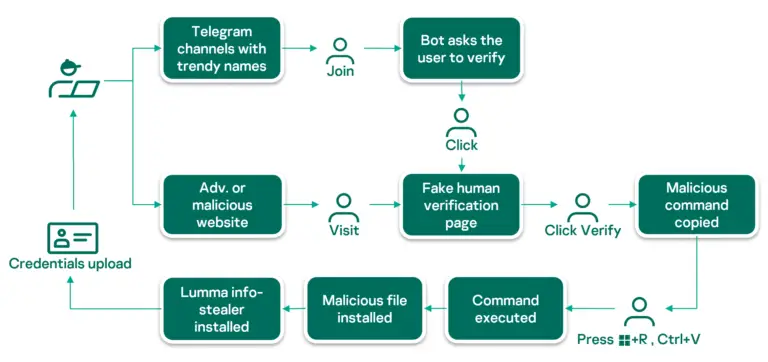
A deep dive into Lumma Stealer's sophisticated techniques: from fake CAPTCHAs to complex infection chains designed to evade detection and steal sensitive data.

CloudSEK's report reveals how fake PDF converters use social engineering to spread malware. Learn how these malicious sites deceive users and steal data

GOFFEE APT is actively targeting Russian organizations with updated tactics, including the new PowerModul implant, sophisticated spear phishing, and lateral movement via custom Mythic agents

Vidar Stealer malware is distributed by masquerading as BGInfo.exe, exploiting expired signatures and file discrepancies to evade detection