
 Do Son
Urgent: Apache CloudStack patches critical flaws (CVE-2026-25199, CVE-2026-25077) enabling VM hijacking and KVM host RCE. Secure your cloud environment now.
Infrastructure Security
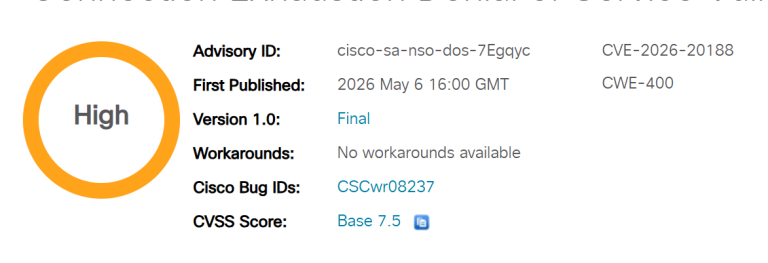
Cisco warns of a critical DoS flaw (CVE-2026-20188) in CNC and NSO. Unauthenticated attackers can freeze network management. Patch to CNC 7.2 or NSO 6.4.1.3 now!

A critical 9.8 CVSS flaw in Convoy (CVE-2026-33746) allows unauthenticated admin access via forged JWTs. Update to v4.5.1 immediately to secure your KVM.

A massive fire at an AWS facility in Bahrain highlights a dangerous shift toward kinetic strikes on cloud infrastructure. Is your multi-region strategy ready?
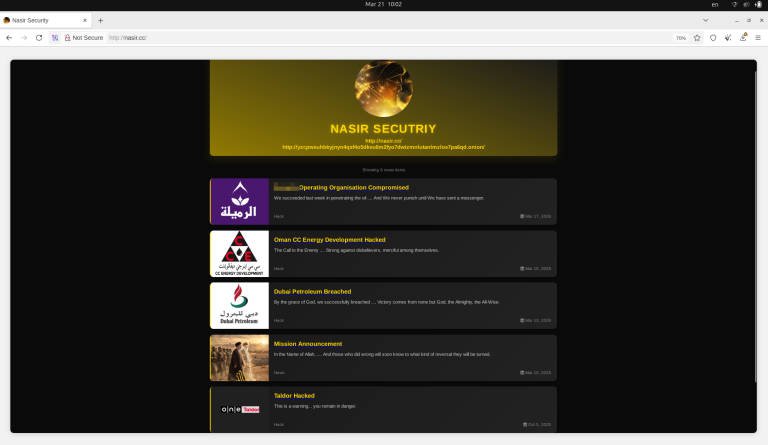
Resecurity uncovers Nasir Security, an Iranian threat actor using supply chain attacks and psy-ops to target Middle East energy vendors and leak blueprints.

HPE Aruba patches a critical 9.8 CVSS bypass in AOS-CX switches that allows unauthenticated password resets. Upgrade to 10.17.1001+ to secure your network now.

Centreon warns of critical AWIE vulnerabilities CVE-2025-15029 (CVSS 9.8) & CVE-2025-15026. Update to v25.10.2 now to prevent unauthenticated SQL injection.
CISA adds critical HPE OneView (CVE-2025-37164) and legacy PowerPoint (CVE-2009-0556) flaws to KEV. FCEB agencies must patch by Jan 28, 2026.
Critical Network Collapse: 9.8 Severity Net-SNMP Buffer Overflow Threatens Global Monitoring Systems

Critical Network Collapse: 9.8 Severity Net-SNMP Buffer Overflow Threatens Global Monitoring Systems
CVE-2025-68615: A critical 9.8 severity Net-SNMP buffer overflow allows attackers to crash snmptrapd. Upgrade to v5.9.5 or v5.10.pre2 immediately!