
 Do Son
Iranian group Seedworm infiltrates global firms using automated Node.js scripts and DLL sideloading via trusted binaries. Protect your credentials now!
Iranian APT
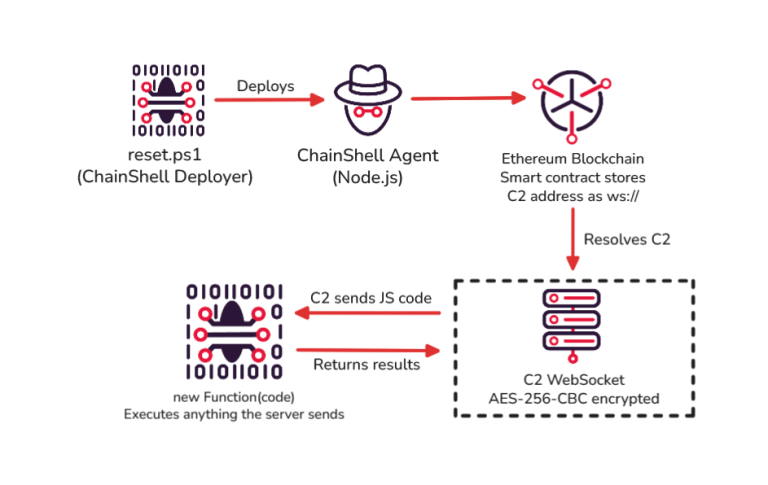
Iranian state actor Muddy Water adopts CastleRAT and ChainShell to hijack browsers and bypass MFA invisibly. A professional-grade shift in APT strategy.

FBI and CISA warn of Iranian APTs hijacking internet-facing PLCs to disrupt U.S. energy and water systems. Learn the 2026 TTPs and how to defend your OT.
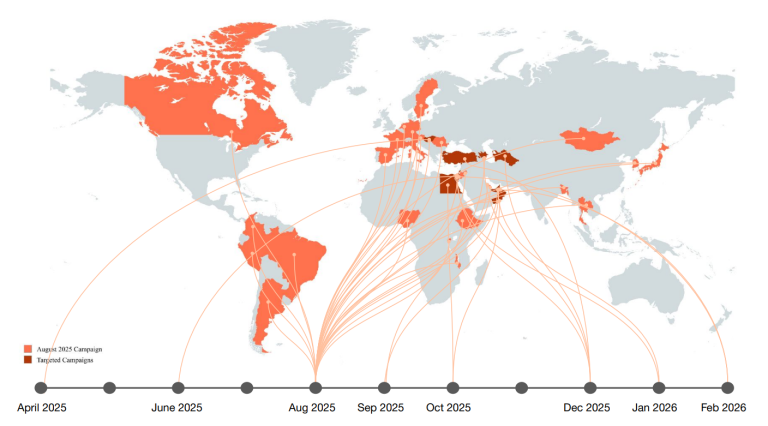
Unit 42 reveals Iranian APT Boggy Serpens is weaponizing hijacked accounts, AI-generated code, and Rust malware to infiltrate critical infrastructure.

Iranian APT Seedworm intensifies cyberespionage against US and Israeli networks using a new stealth backdoor called Dindoor. Read the full threat report.
SafeBreach reveals the return of the Prince of Persia (Infy) group, using Telegram and the new Tonnerre v50 malware to target victims in 2025.

Proofpoint exposed UNK_SmudgedSerpent, an APT using RMM tools (PDQConnect) and M365 spoofs in targeted phishing campaigns against academics and foreign policy experts with complex Iranian political lures.

Iranian-backed "Pay2Key.I2P" ransomware resurfaced on I2P, offering 80% profit for attacks on Western targets. Linked to Fox Kitten & Mimic, it merges cybercrime with geopolitical motives.

Iranian APT "Educated Manticore" (APT42) uses AI-assisted spear-phishing via email/WhatsApp to target critics with React-based phishing kits, bypassing MFA and stealing credentials.
FortiGuard reveals an Iranian APT's multi-stage intrusion into Middle Eastern critical infrastructure using custom malware and stealthy persistence.