 Do Son
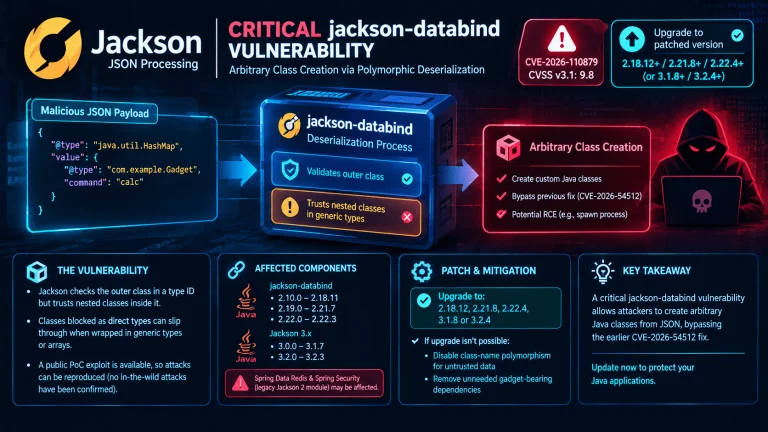
Details and a PoC exploit are public for jackson-databind vulnerability CVE-2026-110879 (CVSS 9.8), a bypass of the CVE-2026-54512 fix. Patch now.
jackson-databind

Aikido Security uncovers the first sophisticated malware on Maven Central: a "prefix swap" attack on the Jackson library used to steal data.