 Do Son
Apache Commons Codec 1.23.0 addresses CVE-2026-119078 and CVE-2026-124077, while Apache HTTP Server 2.4.70 fixes a heap buffer overflow.
Java security
Eight Apache Tomcat vulnerabilities, including a JNDIRealm authentication bypass, are fixed in 11.0.27, 10.1.61 and 9.0.123. Upgrade now.
Struts 7.4.0 fixes four Apache Struts vulnerabilities, including OGNL injection CVE-2026-104711 and a REST plugin DoS. Upgrade now.
Apache Tomcat fixed 11 vulnerabilities on August 25, 2026, including auth bypass (CVE-2026-68569) and HTTP/2 DoS flaws. Update to 11.0.25 now.

Fix dangerous Apache MINA flaws immediately. Learn how a critical deserialization bypass and a DoS vulnerability leave Java applications exposed.
Learn how a new Apache Fory vulnerability impacts Java platforms. Apply the urgent Apache Fory vulnerability patch to protect your enterprise nodes.

CVE-2026-8178 in Amazon Redshift JDBC Driver allows RCE via unsafe class loading. Protect your data warehouse and update to version 2.2.2 now!

Apache Tomcat RCE alert: CVE-2026-34486 exploit code and details are now public. A "fail-open" flaw enables RCE via Tribes clustering. Update immediately.
Apache Wicket 10.9.0 fixes 3 Critical flaws: Path Traversal (CVE-2026-43975), Session Fixation, and Resource Guard bypass. Secure your Java apps and patch now!
Critical 9.0 CVSS flaw in Thymeleaf (CVE-2026-41901) allows SSTI and arbitrary code execution. Secure your Java web apps—upgrade to v3.1.5.RELEASE now!

Apache Thrift v0.23.0 fixes critical Rust DoS, Java MitM, and Node.js path traversal flaws. Secure your cross-language microservices and upgrade immediately!

Apache Neethi v3.2.2 patches critical flaws, including an exponential complexity attack and infinite loops. Secure your Java web services and patch today!
Apache MINA issues emergency patches for two 9.8 CVSS RCE flaws left behind by mistake. Unauthenticated attackers can bypass filters via deserialization.
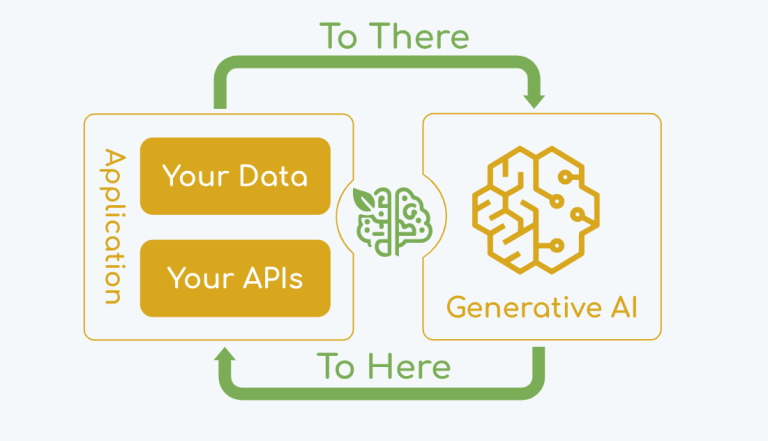
Spring AI discloses two critical injection flaws (CVE-2026-40967 & 40978) in Vector Store implementations. Upgrade to v1.0.6 or v1.1.5 now to prevent data leaks.
Apache MINA (CVE-2026-41635) suffers a critical 9.8 CVSS RCE flaw. Learn how a deserialization filter bypass puts servers at risk and how to patch today.
New Spring Boot flaws (CVSS 9.1) bypass security filters and enable RCE via timing attacks. Impacting versions 2.7.x to 4.0.x—secure your Java apps now.
Critical RCE and XSS vulnerabilities hit Apache ActiveMQ (CVE-2026-41044, 40466). Authenticated attackers can hijack the JVM. Update to 5.19.6 or 6.2.5 now.

Apache HttpClient 5.6 reveals a critical auth flaw (CVE-2026-40542) in SCRAM-SHA-256. Secure your Java microservices—upgrade to 5.6.1 immediately.

Spring Security reveals 7 flaws, including a critical 9.6 CVSS vulnerability in version 7.0. From auth bypass to X.509 impersonation, upgrade to 7.0.5 now.
Thymeleaf 3.1.4 fixes two critical 9.1 CVSS vulnerabilities. Unauthenticated attackers can bypass security for SSTI. Audit your user input and patch today!
Critical 9.3 RCE in OpenAM (CVE-2026-33439) allows unauthenticated attackers to execute OS commands via jato.clientSession. Patch your 16.0.5 servers now!
Qlik issues a critical 9.8 CVSS alert for Talend JobServer and Runtime. Unauthenticated RCE via JMX ports puts data pipelines at risk. Patch immediately.