 Do Son
Apache Wicket vulnerabilities: a security update fixes 19 flaws, including CVE-2026-84170 upload DoS and XSS bugs. Upgrade to 8.20.0, 9.25.0 or 10.12.0.
java
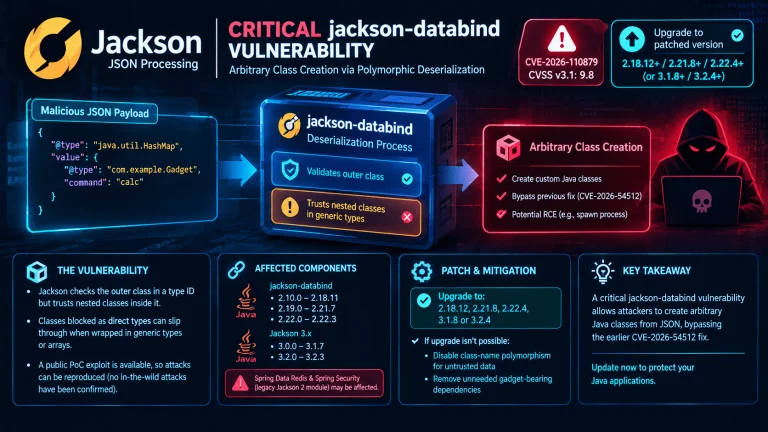
Details and a PoC exploit are public for jackson-databind vulnerability CVE-2026-110879 (CVSS 9.8), a bypass of the CVE-2026-54512 fix. Patch now.
Apache Camel fixes eight Apache Camel vulnerabilities, including XXE flaw CVE-2026-90885 and S3 injection CVE-2026-95664. Upgrade to 4.23.0.
Oracle Java security alert CVE-2026-91403 (CVSS 9.1) distrusts compromised eMudhra intermediate certificates in Java SE and GraalVM. Update now.
Two Apache Jackrabbit vulnerabilities, including critical session hijack flaw CVE-2026-92414 (CVSS 9.3), are fixed. Upgrade to 2.23.6 now.
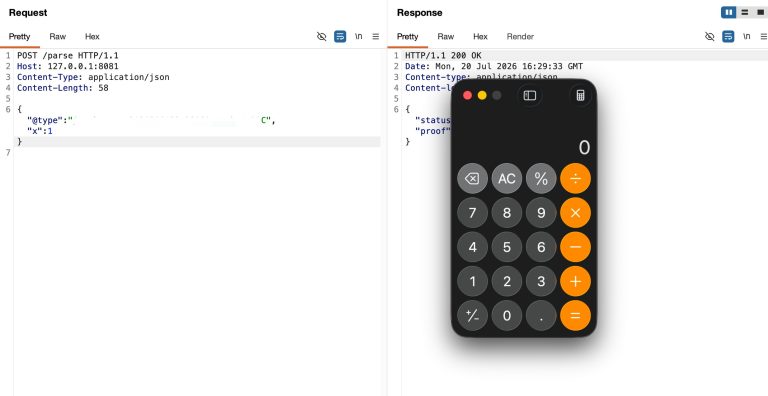
A fastjson RCE hits versions 1.2.68 to 1.2.83 under stock defaults. Details and public PoC code are out, so enable SafeMode or move to fastjson2.

Apache Thrift fixes critical cross-language vulnerabilities (MitM, memory corruption, DoS). Secure your Java, Go, and C++ stacks by upgrading to version 0.23.0.

Critical RCE flaws hit Apache Camel via header injection and unsafe deserialization. Secure your integrations and upgrade to version 4.20.0 today.

GreyNoise reveals a massive Japan-based holiday campaign: 2.5 million attacks targeting 767 CVEs to harvest access for ransomware gangs.

A critical vulnerability in the abandoned lz4-java library exposes apps to DoS. Discover the fix and the mandatory fork migration path here.
CISA, FBI, and NSA call for adopting memory-safe languages (Rust, Go, Java, Swift) to slash software vulnerabilities. Android saw a 52% drop in memory bugs after embracing MSLs.

Apache Tomcat patched four vulnerabilities affecting versions 9.0, 10.1, and 11.0, ranging from DoS to privilege bypass. Update immediately

A flaw (CVE-2025-49146) in PostgreSQL JDBC Driver allows MITM attacks even with channel binding enabled. Upgrade to v42.7.7 or use sslMode=verify-full.

A medium-severity flaw (CVE-2025-41234) in Spring Framework allows Reflected File Download (RFD) attacks. Update to 6.2.8, 6.1.21, or 6.0.29 immediately

A critical XXE vulnerability (CVSS 9.9) in GeoTools llows data disclosure and RCE. Update immediately to patched versions!

Java applications face a critical risk! A flaw in Apache Commons BeanUtils (CVSS 8.8) can lead to arbitrary code execution. Update immediately.

A Spring Framework vulnerability can allow unauthorized access! Learn how it bypasses security annotations and how to fix it.
Critical vulnerability in pac4j Java security framework: CVE-2023-25581 allows attackers to execute arbitrary code on affected systems.
Learn about the TRACTOR program, a DARPA initiative to transition to memory-safe programming languages and automate the conversion of C code to Rust
JetBrains has just released “The State of Developer Ecosystem in 2018” Report, which includes developer preferences for...

Installation & Configuration JDK8 on Ubuntu/Linux Mint