 Do Son
Critical Alert: CVE-2026-43898 (CVSS 10) in SandboxJS allows a total sandbox escape and RCE. Update to version 0.9.6 immediately to secure your host.
JavaScript Security

Urgent: 84 TanStack npm packages hijacked to harvest GitHub Actions secrets. Over 12M weekly downloads impacted. Audit your CI/CD pipelines and rotate tokens.

Critical 9.8 CVSS flaws in vm2 affect 5.7M monthly users, allowing RCE via WASM and Promise bypasses. Upgrade to vm2 v3.11.0 immediately to secure your host.

Critical CVSS 10 and 9.4 vulnerabilities hit n8n. Prototype pollution in XML nodes can lead to full RCE. Patch to v2.18.1 or v1.123.32 immediately.
A critical 9.4 CVSS vulnerability in protobuf.js puts 220 million monthly downloads at risk of RCE. Patch your Node.js and browser apps to version 8.0.1+.

Fastify (25M+ downloads) reveals CVE-2026-33806. A public PoC exploit shows how a single space bypasses schema validation. Upgrade to v5.8.5 now to stay safe.

React patches a 7.5 CVSS DoS vulnerability in Server Components (CVE-2026-23869). Stop CPU exhaustion attacks—update your 19.x dependencies now!
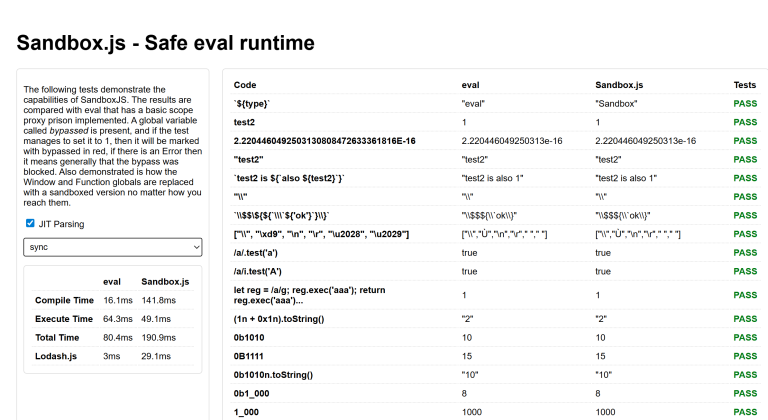
CVE-2026-34208: A critical 10.0 flaw in SandboxJS allows code to escape and poison host objects like Math.random. Secure your environment—update immediately!
Node.js releases critical updates for 20.x to 25.x, fixing high-severity flaws like the __proto__ header crash and TLS errors. Update to v25.8.2 now.

A critical 9.6 CVSS vulnerability in jsPDF (CVE-2026-31938) allows attackers to inject malicious scripts via XSS. Update to version 4.2.1 immediately.
Critical 10.0 CVSS flaw in SandboxJS (CVE-2026-26954) allows attackers to escape the sandbox and achieve Remote Code Execution. Patch to version 0.8.34 now.

Tenable uncovers "ambar-src," a malicious npm package mimicking "ember-source." It uses preinstall scripts to deploy reverse shells and Apfell malware.

Critical prototype pollution flaw (CVE-2026-27212) in the Swiper npm package allows RCE, DoS, and auth bypass. Update to version 12.1.2 immediately.
A critical PDF Object Injection flaw (CVE-2026-25755) in jsPDF allows attackers to bypass AcroJS sandboxes. Update to version 4.2.0 immediately.
Critical SandboxJS flaw CVE-2026-25881 allows sandbox escape via prototype pollution. Malicious code can modify host logic & execute RCE. Update to v0.8.31.

Axios flaw CVE-2026-25639 (CVSS 7.5) crashes Node.js servers via malicious JSON. Attackers use __proto__ to trigger DoS. Update to v1.13.5 now.
Critical SandboxJS flaws (CVSS 10.0) allow sandbox escape & host takeover via prototype pollution. Update to v0.8.29 immediately to stop code execution.

Critical Orval flaw CVE-2026-25141 (CVSS 9.3) allows code injection via OpenAPI comments. 2.8M+ downloads affected. Update to v7.21.0 now.
CVSS 10 flaw CVE-2026-23830 in SandboxJS allows RCE via unpatched Async functions. Attackers bypass all limits. Update to v0.8.26 immediately.

CVSS 9.8 vm2 flaw (CVE-2026-22709) affects 3.7 million users, allowing total sandbox escape via async functions. Update to v3.10.2 immediately.
New React Server Components flaw CVE-2026-23864 (CVSS 7.5) exposes apps to DoS attacks. Previous patches were incomplete. Update to v19.0.4+ now.

Critical binary-parser flaw CVE-2026-1245 allows code injection in Node.js. Versions < 2.3.0 are vulnerable to RCE. Update to v2.3.0 immediately.