 Do Son
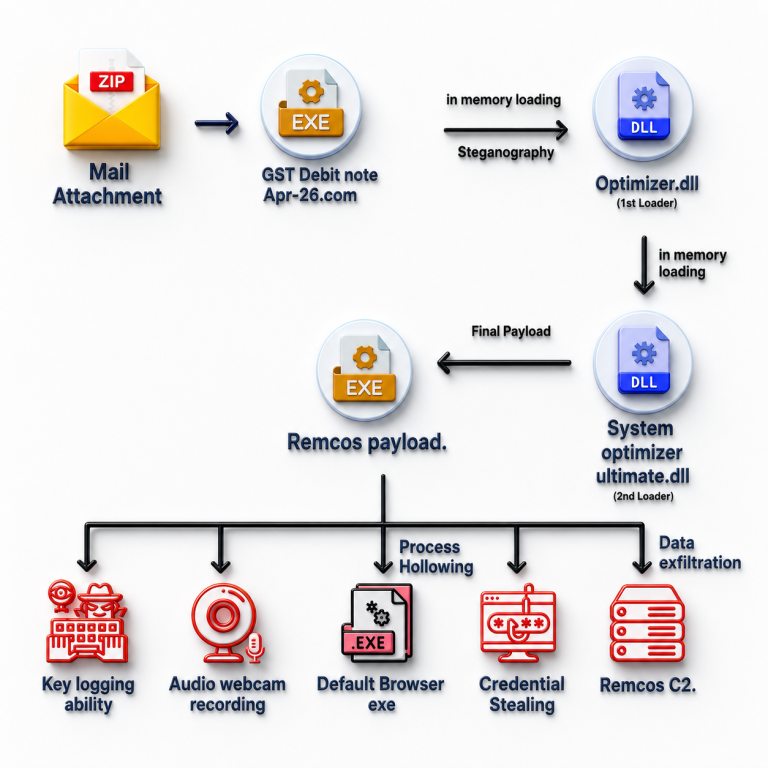
A steganographic loader hides Remcos RAT inside a bitmap and runs it in memory. K7 ties the fileless campaign to India via fake GST lures.
K7 Security Labs

Researchers unmask ResokerRAT, a stealthy Trojan using Telegram to spy on systems and block security tools like Task Manager. Is your PC calling home?

Phantom v3.5 info-stealer targets passwords and crypto via a fake Adobe installer. It uses SMTP to exfiltrate data directly to attackers.

Patchwork APT has launched a new campaign in South Asia, exploiting DLL sideloading and obfuscation to deliver malware that masquerades as VLC media player for deep espionage.