 Do Son
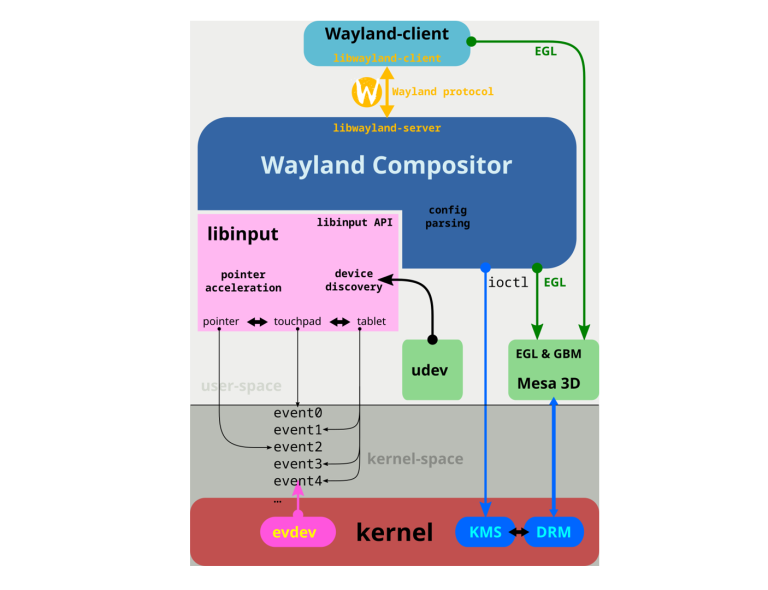
Critical 8.8 CVSS flaw in libinput allows sandbox escape via malicious Lua plugins. Affects GNOME, KDE, and Fedora. Update to 1.31.1 or 1.30.3 now!
kde
A critical Konsole vulnerability allows arbitrary code execution via a telnet:// URL scheme. Linux users must update to 25.04.2 immediately.

The KDE development team has issued a critical security advisory warning users of a high-severity vulnerability (CVE-2024-36041)