 Do Son
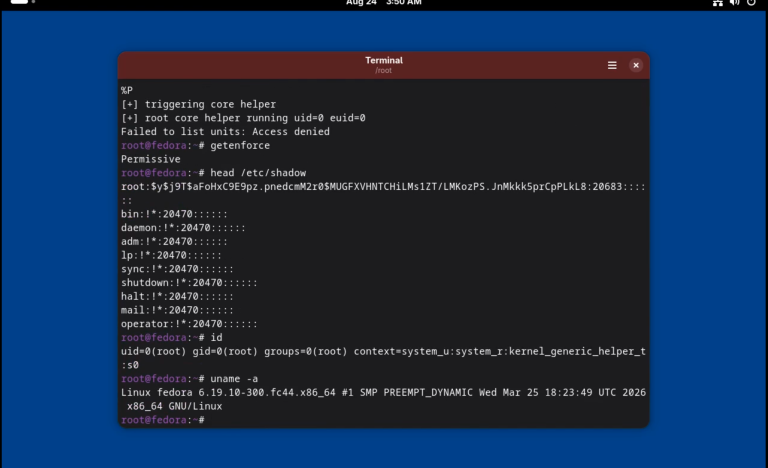
A public proof-of-concept for the CVE-2026-52933 privilege escalation flaw is available. This Linux kernel io_uring exploit carries a CVSS 7.8 score.
Kernel Exploit
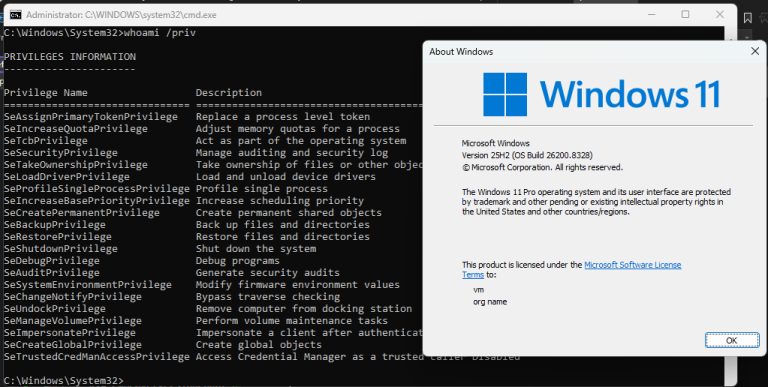
A dangerous Windows Kernel EoP vulnerability allows browser sandbox escapes. Public PoC exploit code is available on GitHub.
Apple releases emergency iOS 15.8.7 and 16.7.15 updates for older iPhones to block the actively exploited "Coruna" WebKit and Kernel exploit kit. Patch now.
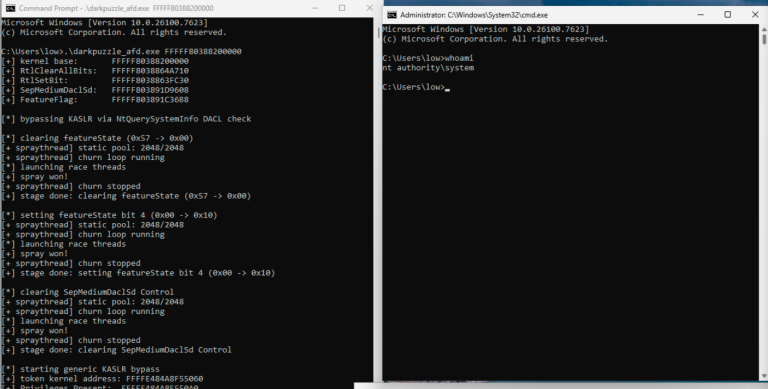
Windows kernel vulnerability CVE-2026-21241 (afd.sys) exposed! A new PoC exploit shows how local attackers can win a race condition to gain SYSTEM privileges.

A Windows Agere Modem EoP flaw (CVE-2025-24990) under active exploit allowed arbitrary kernel R/W even when unused. Microsoft removed the driver in the October update. PoC is available.

A kernel-level UAF flaw (CVE-2025-38001) in Linux HFSC/NETEM allows root privilege escalation via RBTree manipulation. PoC available. Update now!

PoC reveals how a Linux vsock driver flaw enables local users to escalate privileges to root via a dangerous Use-After-Free vulnerability.

PoC for CVE-2023-41992 reveals iOS kernel flaw enabling local privilege escalation. Apple patched it, but risks persist for outdated devices.

CVE-2024-26809 affects Linux nftables with a double-free bug in nft_pipapo_destroy, enabling kernel-level exploitation and potential root access.

A vulnerability (CVE-2024-53141) in the Linux kernel's ipset component allows for privilege escalation and kernel-level code execution.