 Do Son
TL;DR Federal officials warned organizations about seven newly abused security flaws. The agency confirmed that threat actors...
KEV
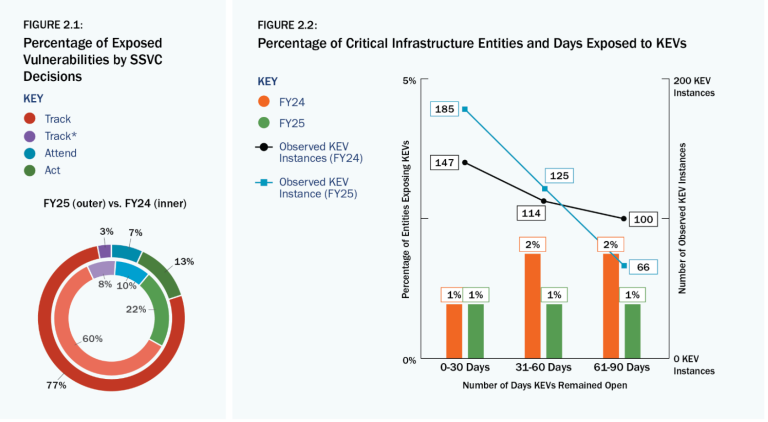
The newly published CISA Vulnerability Review for fiscal years 2024 and 2025 delivers a blunt message: the...
TL;DR The CISA KEV catalog gained two entries on July 15, 2026. The agency confirmed active exploitation...
TL;DR CISA has confirmed active exploitation of three SharePoint vulnerabilities: CVE-2026-32201, CVE-2026-45659, and CVE-2026-56164. Threat actors chain...
State of Exploited Vulnerabilities — Q2 2026 Coverage period: April 1 – June 30, 2026 Data source:...

Three new vulnerabilities in Qualcomm’s Adreno GPU driver have been added to CISA’s Known Exploited Vulnerabilities (KEV)...
The U.S. National Institute of Standards and Technology (NIST) is proposing a metric to address one of...

The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent alert, adding CVE-2021-20035 to its Known...

Two critical vulnerabilities in Sitecore’s anti-CSRF module have re-emerged as active threats, with proof-of-concept exploits in circulation...
Cybersecurity and Infrastructure Security Agency (CISA) has added two critical security vulnerabilities to its Known Exploited Vulnerabilities...

The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent warning about two critical security vulnerabilities...

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2023-28461, a high-severity security flaw impacting Array...
Critical flaws in widely-used networking and security products demand immediate attention from administrators. The Cybersecurity and Infrastructure...

The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent alert regarding the active exploitation of...

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has once again raised the alarm, adding four new...

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning to federal agencies and organizations...

A high-severity vulnerability (CVE-2024-8190) in Ivanti Cloud Services Appliance (CSA) is under active exploitation, prompting an urgent...

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning, adding three actively exploited vulnerabilities...

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned of a critical security vulnerability affecting SolarWinds Web...

Microsoft’s August 2024 Patch Tuesday release addresses 88 vulnerabilities, including seven critical flaws and 10 zero-day vulnerabilities....

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent warning regarding two actively exploited...

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent warning regarding a critical vulnerability...