 Do Son
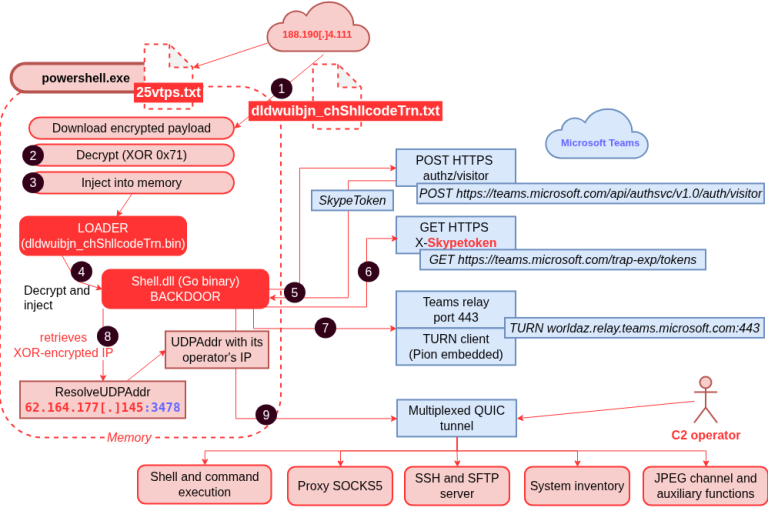
A new DragonForce backdoor hides in Microsoft Teams TURN relays and falls back to MQTT. See how it works and how defenders can spot it.
Lab52
LAB52 uncovers the DRILLAPP backdoor, a novel espionage campaign targeting Ukraine that weaponizes Microsoft Edge for screen recording and surveillance.

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.

APT28's "Operation MacroMaze" targets Europe using Spanish gov decoys. The campaign uses "low-tech" macros & Webhook.site to evade detection.

New "APT IRAN" framework targets energy grids & military networks. Lab52 links the tool to the IRGC. See the threat to critical infrastructure.