 Do Son
IBM fixes 25 Langflow vulnerabilities, including critical RCE flaw CVE-2026-104334 (CVSS 9.8). Upgrade to Langflow 1.12.3 now.
Langflow
A critical Langflow SSRF flaw (CVE-2026-12944) exposes cloud credentials and internal networks. Patch your Langflow OSS servers immediately.
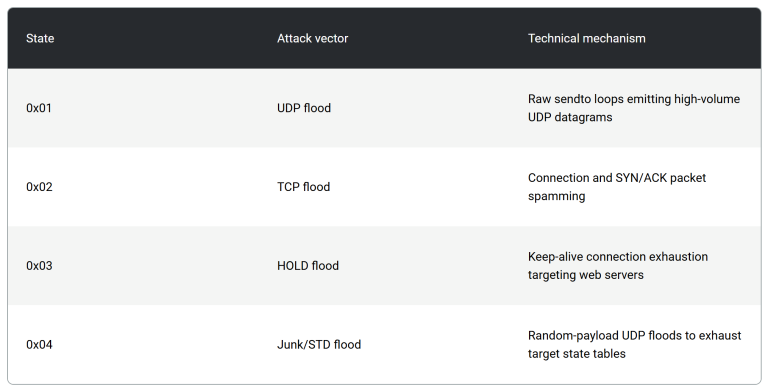
Attackers exploit a Langflow RCE flaw to drop a custom Gafgyt botnet built purely for DDoS, Akamai reports. The payload hides C2 with a modified RC4 cipher.
CISA added four flaws to its KEV catalog, including WordPress RCE (CVE-2026-63030) and Langflow RCE (CVE-2026-0770). All are exploited in the wild.
Sysdig documented JADEPUFFER, the first agentic ransomware run end-to-end by an AI agent. It breached Langflow via CVE-2025-3248 and extorted a database.
CISA added four actively exploited flaws to its KEV Catalog, including critical Joomla, Langflow, and ColdFusion bugs. Agencies must patch by July 10.
Multiple Langflow OSS vulnerabilities, including the critical CVE-2026-10134 flaw, expose servers to code execution. Patch immediately.
A new Langflow cryptominer malware campaign exploits CVE-2026-33017 to deploy malicious payloads. Learn how this threat spreads and how to stay protected.
Three critical Langflow security vulnerabilities (CVE-2026-55255, CVE-2026-55447, CVE-2026-55450) expose AI applications to RCE and DoS attacks. Patch now.
A critical Langflow RCE vulnerability (CVE-2026-10561) scores CVSS 10 and enables unauthenticated remote code execution. Upgrade to 1.9.4 now.
A critical Langflow file upload flaw (CVE-2026-55450) is public with a PoC, enabling unauthenticated denial-of-service and path disclosure. Patch 1.9.1.
A critical Langflow RCE vulnerability impacts the Shareable Playground feature. Learn about the new security patches available.
CISA updates its KEV Catalog with critical flaws in Langflow (CVE-2025-34291) and Trend Micro Apex One. Federal agencies ordered to patch by June 4, 2026.

Sysdig exposes "NATS-as-C2" infrastructure exploiting Langflow RCE (CVE-2026-33017). Learn how to defend your AI pipelines and block the exploit.
Langflow patches a critical 9.6 CVSS path traversal vulnerability (CVE-2026-42048). Learn how an unsafe bulk delete function put entire filesystems at risk.
1,740 new vulnerabilities, 147 critical. From F5 crashes to a Trivy supply chain attack, here’s your high-priority triage list for March 2026.
Two critical flaws in Langflow (CVE-2026-33017 & CVE-2026-33309) allow unauthenticated remote code execution and arbitrary file writes. Secure servers now.
Langflow 1.8.0 patches a critical 9.8 CVSS RCE vulnerability (CVE-2026-27966) where a hardcoded "allow_dangerous_code" setting enables prompt injection attacks.

The Langflow project has issued an important security advisory regarding a newly discovered vulnerability that poses a...
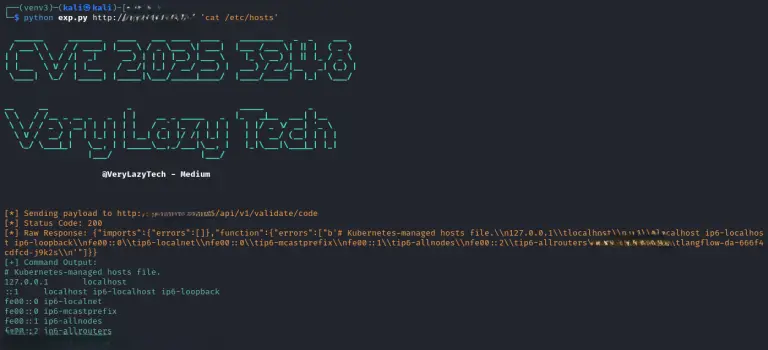
A critical RCE flaw (CVE-2025-3248) in Langflow is being actively exploited to deploy the stealthy Flodrix botnet for reconnaissance and diverse DDoS attacks on AI app servers.

CISA alerts to active exploitation of CVE-2025-3248 in Langflow. Unauthenticated RCE vulnerability poses high risk. Upgrade to 1.3.0 immediately.
A critical vulnerability (CVE-2025-3248) in Langflow allows unauthenticated remote attackers to fully compromise servers. Users are urged to upgrade to version 1.3.0 or restrict network access