 Do Son
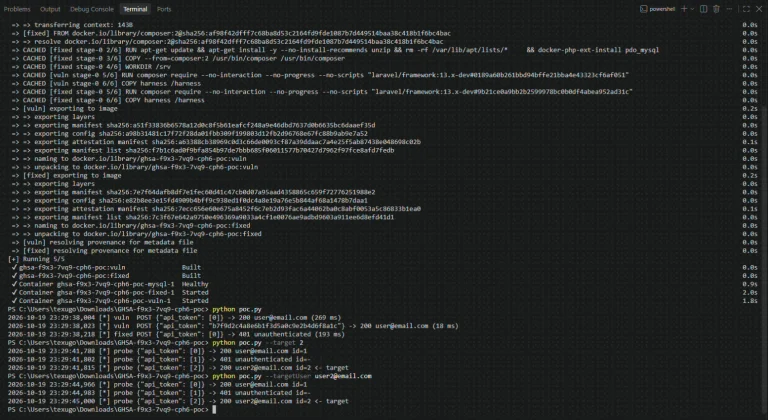
A public PoC is out for CVE-2026-114509, a Laravel authentication bypass in TokenGuard enabling account takeover. Upgrade to 12.68.0 or 13.29.0.
Laravel
A critical Laravel authentication bypass (CVSS 9.2) in TokenGuard enables account takeover without a token. Upgrade to 13.29.0 or 12.68.0.

A suspected Indonesian threat actor exploited the Laravel Livewire vulnerability (CVE-2025-54068) to steal credentials from over 6,000 web applications.
Laravel Passport patches a 7.1 CVSS authentication bypass where machine tokens masquerade as human users. Protect your app—upgrade to v13.7.1 now!

Laravel Reverb flaw CVE-2026-23524 (CVSS 9.8) puts 7M apps at risk of RCE via Redis. Update to v1.7.0 or disable scaling now to stay secure.

Unpatched Livewire Filemanager flaw (CVE-2025-14894) allows unauthenticated RCE via malicious uploads. Check storage:link configurations immediately.

Synacktiv unmasks CVE-2025-54068, a critical Livewire hydration flaw, and Livepyre, a tool that achieves RCE even if the APP_KEY is known.

A critical RCE (CVE-2025-54068) in Livewire v3.6.3 and earlier allows unauthenticated attackers to execute arbitrary code on millions of Laravel applications. Update now!

A critical SSTI flaw (CVE-2025-53833, CVSS 10.0) in LaRecipe allows unauthenticated RCE on affected servers via template injection. Update to v2.8.1 immediately!
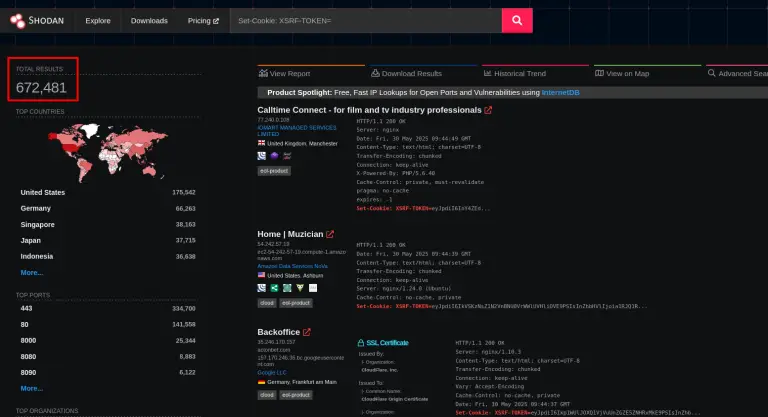
Synacktiv reveals Laravel’s APP_KEY vulnerability allows RCE via deserialization attacks when the key is leaked or guessable, risking full application compromise.

Critical CVSS 9.9 RCE, IDOR, and path traversal flaws in InnoShop with full PoC exploit. No patch available—eCommerce sites at serious risk.

A critical Auth0 PHP SDK deserialization flaw (CVE-2025-48951, CVSS 9.3) allows unauthenticated RCE in web apps. Patch to v8.14.0+ immediately!

Critical vulnerabilities discovered in Voyager, an open-source Laravel admin panel. Learn about the CVE-2024-55417 flaws and their impact on website security.

Discover the CVE-2024-53353 vulnerability in Invoice Ninja that could allow attackers to access sensitive files.

Learn about the critical security vulnerability, CVE-2024-52301, in Laravel framework. Discover how this issue could expose applications to unauthorized access and data tampering.

Learn about CVE-2024-47823, a critical vulnerability in Livewire framework for Laravel, allowing remote code execution via file uploads.