 Do Son
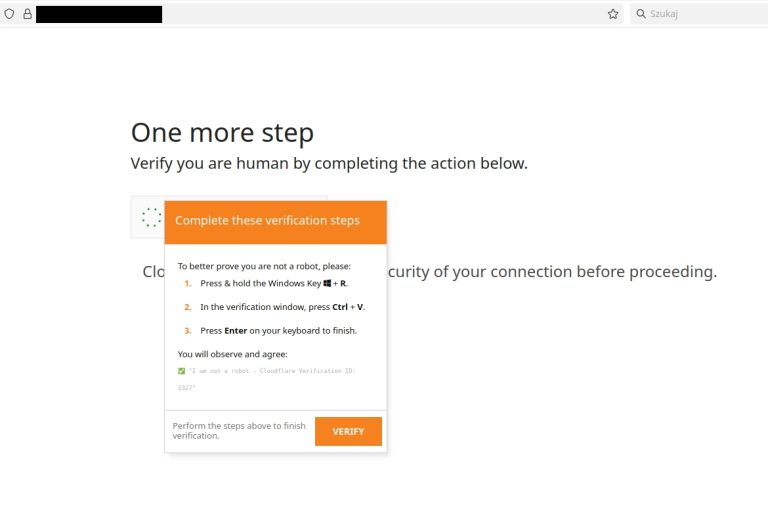
CERT Polska reveals how a fake "ClickFix" CAPTCHA campaign tricked users into deploying evasive Latrodectus and Supper malware. Protect your network now.
Latrodectus
Zscaler ThreatLabz has uncovered a new backdoor malware, YiBackdoor, that shares extensive code with IcedID and Latrodectus and is being tested for ransomware ops.

Uncover the latest cyber threat: LUNAR SPIDER. Learn about their tactics and the adoption of Brute Ratel C4 in their malvertising campaigns.

Discover Pronsis Loader: A Java implementation of PHP malware that poses a significant risk. Learn about its similarities to D3F@ck Loader.

In a joint report by Proofpoint's Threat Research team and Team Cymru, a potent new malware dubbed "Latrodectus" has been exposed