
 Do Son
Gen Labs exposed Kimsuky deploying HttpTroy via fake VPN lures and Lazarus using an upgraded BLINDINGCAN RAT. Both North Korean APTs use DLL sideloading and custom crypto to evade analysis.
Lazarus Group

Lab52 exposed Lazarus Group using DreamLoader malware via fake job lures. The modular tool chain abuses DLL sideloading and the Microsoft Graph API for stealthy C2 communications.

The Lazarus Group is using a new campaign to steal crypto by exploiting a vulnerability (CVE-2025-48384) with fake interviews and poisoned code repositories.

A new report reveals that the Lazarus Group is actively monitoring CTI platforms to evade detection and sustain a ClickFix phishing campaign against the cryptocurrency sector.

A new report reveals a Lazarus Group subgroup is using a tiered arsenal of custom RATs—PondRAT, ThemeForestRAT, and RemotePE—to target the financial and crypto sectors.

North Korean IT workers are using deepfakes and fake identities to secure remote jobs, funding their regime’s weapons programs while posing a major security threat.

North Korea's Lazarus Group is waging a covert cyberespionage campaign, poisoning 234+ open-source packages on npm/PyPI to steal secrets from CI/CD pipelines and developer environments.

Taiwan's BitoPro exchange confirms North Korea's Lazarus Group stole $11.5M in crypto via phishing an employee and bypassing MFA on AWS infrastructure.

BitMEX security team infiltrates Lazarus Group's infrastructure after a phishing attempt, exposing their tactics and even a hacker's real location.

Silent Push uncovers Lazarus Group's campaign using fake crypto job offers to spread malware (BeaverTail, InvisibleFerret, OtterCookie), targeting job seekers.

Kaspersky uncovers "Operation SyncHole," a sophisticated cyber-espionage campaign by the Lazarus Group targeting critical South Korean sectors using advanced malware.

Threat actors abuse Microsoft’s mavinject.exe to inject malicious DLLs into trusted processes, evading detection in stealthy APT campaigns.

Explore the RedHat Hacker and the Lazarus Group’s recent attack strategies on Windows web servers for command-and-control infrastructure.

Explore Lazarus' latest campaign targeting the npm ecosystem with six malicious packages threatening developer security.
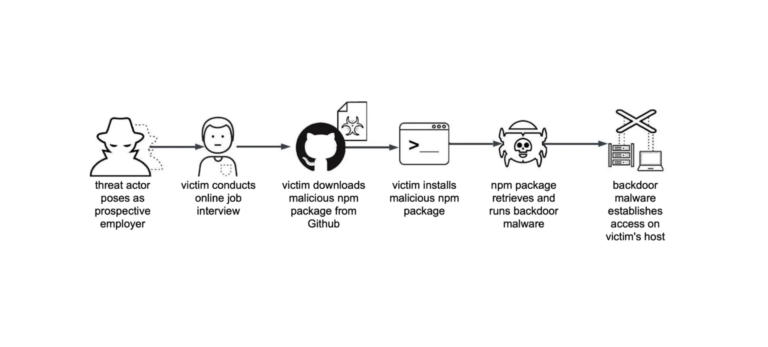
Uncover the dangers of Lazarus Group’s Infostealer Malware targeting software developers and IT professionals with malicious scripts.
Beware of cyber espionage on LinkedIn! Lazarus Group targets professionals with fake job offers and sophisticated malware.

Uncover the details of Operation Phantom Circuit, a highly sophisticated cyber espionage campaign orchestrated by North Korea's Lazarus Group.

Discover the latest supply chain attack orchestrated by the North Korean APT Lazarus Group. Learn how the BeaverTail malware infiltrates developer environments.

Uncover the sophisticated RID Hijacking technique used by the Andariel threat group. Learn how this technique allows attackers to escalate privileges during breaches.

Stay informed about the escalating threat of cryptocurrency thefts by North Korean cyber actors. Learn about their malicious activities and the impact on the global financial system.

Discover the sophisticated tactics of the Lazarus Group in their latest DeathNote Campaign. Learn how they exploit fake job opportunities to infiltrate defense, aerospace, cryptocurrency, and nuclear sectors.

Discover the stealthy technique used by the Lazarus Group: RustyAttr. Learn how this method leverages macOS metadata to conceal malicious payloads.