 Do Son
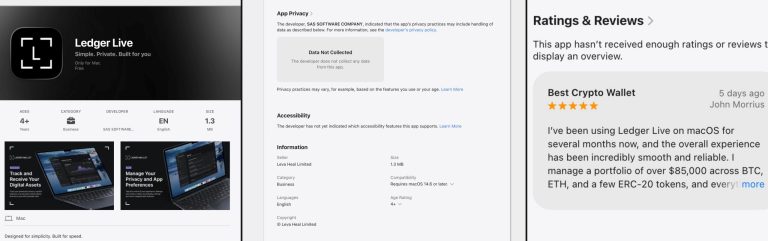
A malicious fake Ledger Live app on the Mac App Store has stolen $9.5M from users. Learn how the scam bypassed Apple's security and why your seed phrase is at risk.
Ledger Live

Intego exposes a malicious Ledger Live app for macOS. Using weaponized Electron ASAR archives and a TLS bypass, OSX/Amos silently siphons your seed phrases.
Beware of "MacSync Stealer": A new macOS malware campaign using SEO poisoning and terminal commands to hijack crypto wallets and system keys.
New "Matryoshka" Mac malware uses "ClickFix" scams to steal crypto. Intego warns of fake error fixes patching Ledger & Trezor apps. Stay alert.

A new macOS stealer (Nova) uses LaunchAgents to install a modular backdoor. Its main function is replacing legitimate Ledger/Trezor apps with phishing clones that exfiltrate seed phrases as users type.

Jamf exposed DigitStealer, an advanced macOS infostealer that checks for Apple M2+ chips. It uses Cloudflare Pages for delivery, JXA for stealth, and modifies Ledger Live to steal crypto wallets via DNS TXT C2.

Jamf Threat Labs has uncovered a sophisticated new macOS infostealer variant that managed to bypass Apple’s security defenses by leveraging valid code signing and notarization

A new macOS information stealer, a potential AMOS variant, targets crypto users and Ledger Live accounts, stealing passwords and wallet data using stealthy daemonization and local admin prompt tactics.