 Do Son
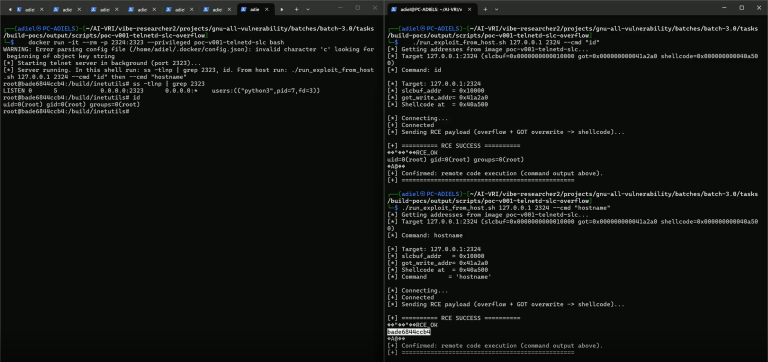
A critical 9.8 CVSS pre-auth buffer overflow in GNU Inetutils telnetd allows attackers to execute arbitrary code and gain root access. Patch immediately.
legacy systems

Debian Linux is proactively addressing the Year 2038 Problem by adopting a 64-bit time_t format on 32-bit architectures, preparing for the timestamp overflow set to impact legacy systems globally.

ABB's ASPECT BMS has 32 security flaws, with some critical RCE and privilege escalation vulnerabilities having no planned fixes for legacy systems.

CISA warns of potential risks from Oracle cloud credential exposure. Urges password resets, MFA, and vigilance against phishing attacks.