
 Do Son
A LNK phishing attack drops a Node.js backdoor and hides its C2 on the TON blockchain using EtherHiding, LevelBlue reports.
LevelBlue
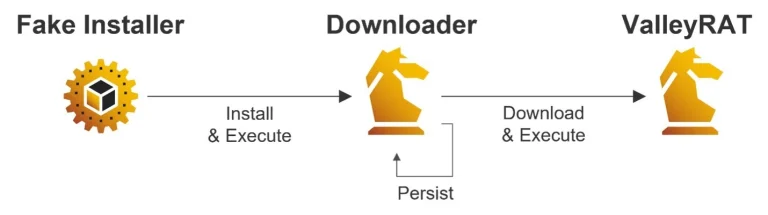
LevelBlue tracks a ValleyRAT malware email campaign using DLL sideloading and fileless execution to hit Japanese and Chinese users.
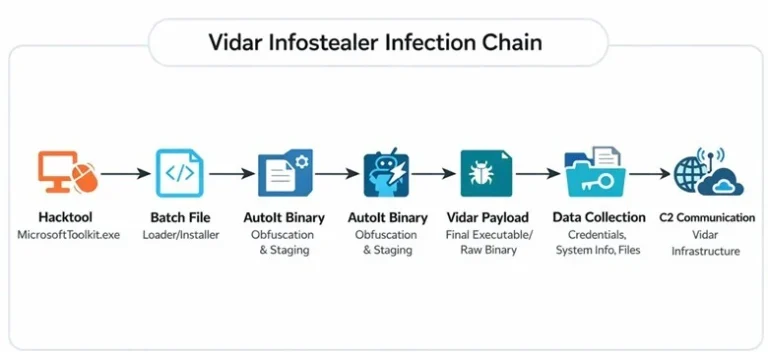
LevelBlue unmasks a stealthy Vidar Stealer campaign using AutoIt scripts and file renaming tricks to bypass EDR and harvest credentials. Is your system at risk?

LevelBlue uncovers MioLab (Nova), a premium macOS MaaS targeting crypto wallets, Keychains, and Apple Notes. Protect your BIP39 seeds and Mac today.
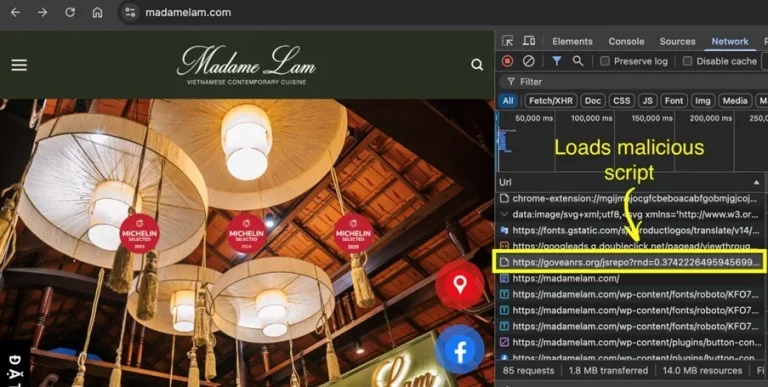
LevelBlue warns of StealC malware using "ClickFix" fake CAPTCHAs. Users are tricked into running fileless malware via PowerShell. Stay alert.