
 Do Son
ENKI WhiteHat traced a Kimsuky Gomir variant into South Korean groupware vendors, plus a new DriveTroy backdoor that hides its C2 in Google Drive.
Linux Backdoor

Harvester APT expands to Linux using Microsoft Graph API for C2. Learn how the "GoGra" variant uses Outlook and "Zomato Pizza" lures to evade detection.
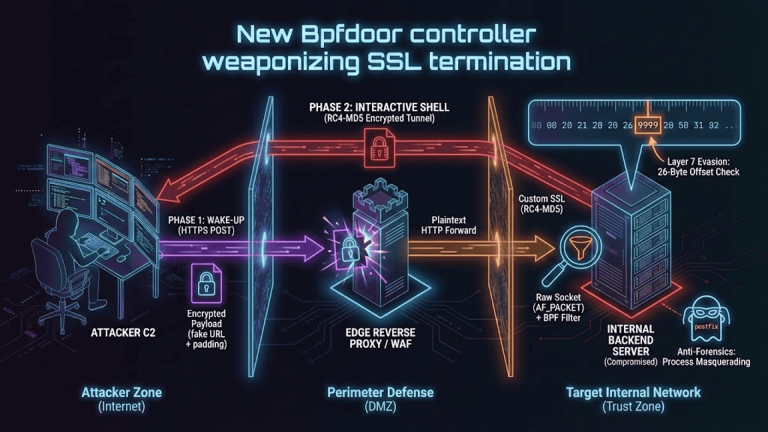
Rapid7 uncovers Red Menshen’s BPFdoor backdoor in global telecom cores. Learn how this China-nexus actor uses kernel-level stealth for mass surveillance.

A previously undetectable Linux backdoor called GhostPenguin was exposed by AI-driven threat hunting. The C++ malware uses RC5-encrypted UDP for stealthy, multi-threaded C2 operations.

Learn about Auto-Color, a stealthy Linux backdoor targeting government and educational institutions across continents.

The North Korean state-sponsored group Springtail (also known as Kimsuky) has added a new Linux backdoor, dubbed Gomir, to its arsenal