 Do Son
Stay up to date with the latest news on a critical Linux vulnerability. Learn about its severity, impact, and ongoing efforts to find a fix.
Linux

Discover the latest statistics on Linux market share. See how it has reached an unprecedented 4.44% in July and the reasons behind its growth.
Cheana Stealer Targets VPN Users Across Windows, Linux, and macOS in Sophisticated Phishing Campaign
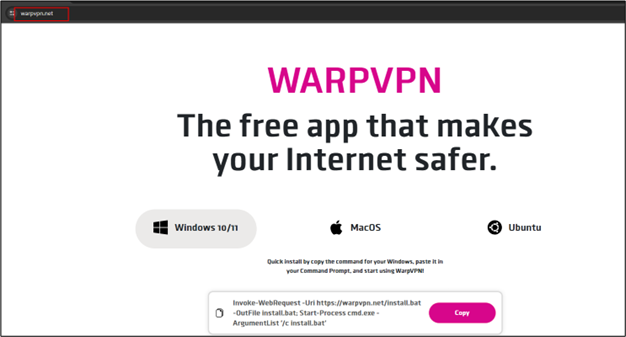
Cheana Stealer Targets VPN Users Across Windows, Linux, and macOS in Sophisticated Phishing Campaign
Protect yourself from the Cheana Stealer, a malicious tool targeting VPN users. Learn how to recognize and defend against this new cyber threat.

Learn about Debian 11 LTS and its extended security support phase. Find out how it ensures usability and provides five years of security updates

Learn about the serious security flaw in Flatpak (CVE-2024-42472) and how it allows unauthorized access to files outside the sandbox.

The espionage group Daggerfly has also introduced a new Windows backdoor, Trojan.Suzafk, first documented by ESET in March 2024

Google Chrome 127 brings a host of improvements, prominently featuring 24 security-related fixes, available for Windows, macOS, and Linux

Halcyon's research team has identified a new ransomware group dubbed "Volcano Demon," responsible for a series of recent attacks

Victims whose files have been encrypted by the Mallox ransomware Linux variant may be able to recover their data using the decryptors

TRU has detailed a CVE-2024-6387 flaw, dubbed 'regreSSHion,' that leaves millions of Linux systems vulnerable to remote code execution

A new ransomware-as-a-service (RaaS) called RansomHub has emerged, targeting Windows, Linux, and ESXi operating systems

Trend Micro's threat-hunting team has uncovered a new Linux variant of the TargetCompany ransomware, marking a significant escalation
Security researcher published the technical details and a proof-of-concept (PoC) code for a vulnerability, identified as CVE-2023-3390

The vulnerability (CVE-2024-33899 for Linux/Unix, CVE-2024-36052 for Windows) poses a greater threat on Linux and Unix
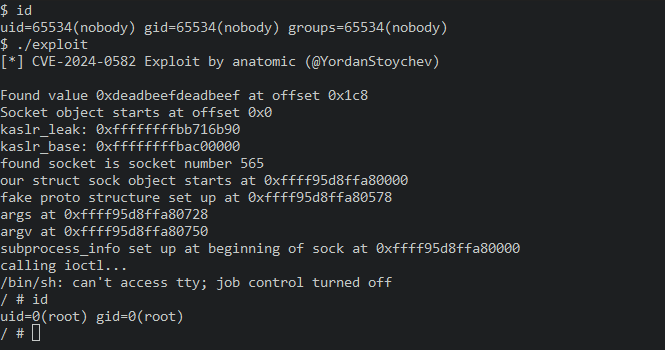
Researchers have provided a detailed analysis of the CVE-2024-0582 vulnerability, including a proof-of-concept (PoC) exploit
CVE-2024-28085: Critical ‘WallEscape’ Flaw Discovered in Linux Utilities Package – Passwords at Risk

CVE-2024-28085: Critical ‘WallEscape’ Flaw Discovered in Linux Utilities Package – Passwords at Risk
A serious security vulnerability, dubbed "WallEscape" (CVE-2024-28085), has been uncovered in the essential Linux system utilities package

Researchers have uncovered a new security vulnerability dubbed "GhostRace" (CVE-2024-2193) that allows attackers to exploit weaknesses

two (CVE-2024-1929, CVE-2024-1930) critical vulnerabilities could allow attackers to gain complete control of affected systems

CVE-2023-52160, CVE-2023-52161 in WiFi software are allowing attackers to trick victims into connecting to evil twins of trusted networks

The GNU C Library (glibc), a fundamental component in major Linux distributions, has a critical vulnerability, CVE-2023-6246

Identified with a CVSS score of 8.3, CVE-2023-40547 exposes a remote code execution vulnerability within Shim.

CVE-2023-4001 is an authentication bypass flaw in GRUB. GRUB is the gatekeeper of the booting process in many UEFI-based computers