 Do Son
A new StopRansomware advisory warns SafePay ransomware has hit 600+ victims via VPN logins and edge flaws. See its tactics and key defenses.
living-off-the-land
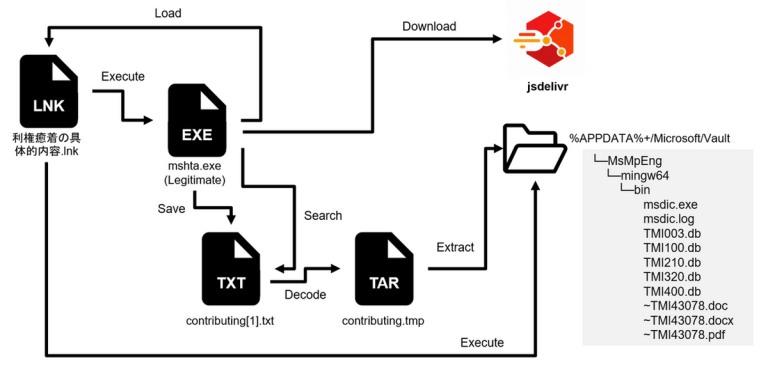
JPCERT/CC details new APT-C-60 attacks on Japan. The group abuses Proton Drive, LNK files, and GitHub to deploy SpyGlace malware.

Seqrite ties a Rare Werewolf phishing campaign to Russian aerospace firms, using a fake invoice to plant AnyDesk for stealthy remote access.

G Data uncovers a new Remcos RAT variant using DonutLoader shellcode and trusted LOLBins to bypass Windows security filters.
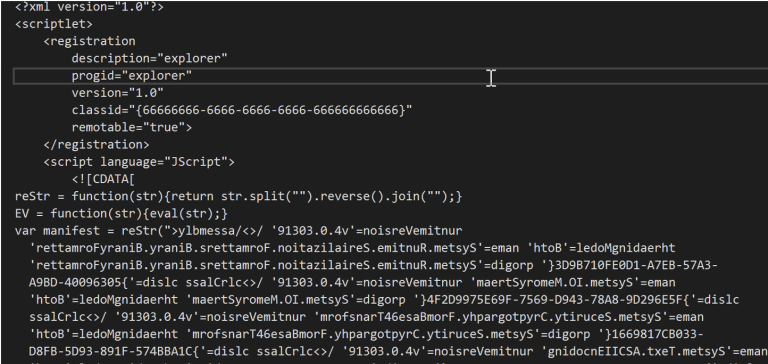
Darktrace exposes Chinese APT Twill Typhoon’s latest campaign using DLL sideloading and Yahoo/Apple CDN lookalikes to deploy a modular .NET RAT.
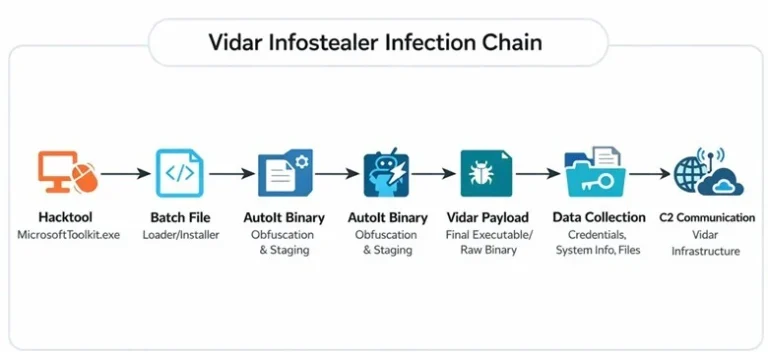
LevelBlue unmasks a stealthy Vidar Stealer campaign using AutoIt scripts and file renaming tricks to bypass EDR and harvest credentials. Is your system at risk?
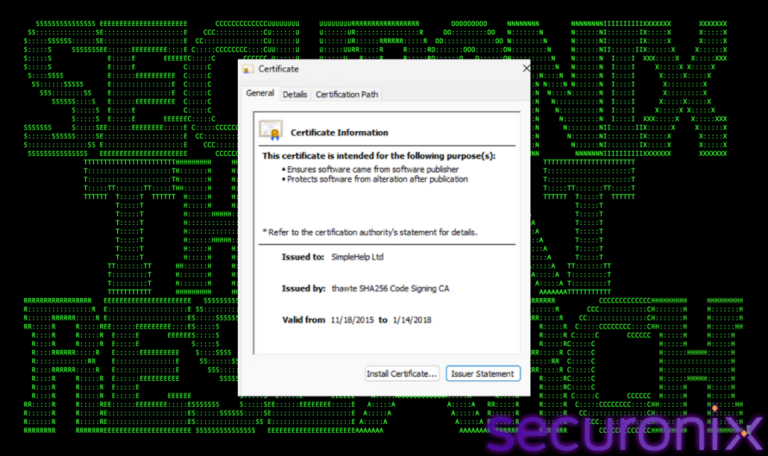
Securonix exposes an 80+ organization breach using "self-healing" RMM tools and Safe Mode persistence. Standard antivirus is blind—learn how to hunt it!
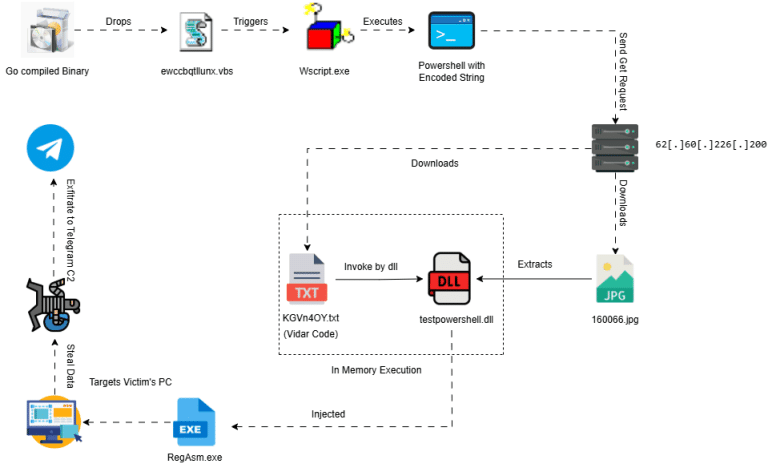
Vidar infostealer evolves into a fileless 2026 threat. From fake CAPTCHAs to "Claude Code" leaks, see how it steals crypto and passwords via Telegram C2.

Microsoft Defender warns of a 2026 WhatsApp malware campaign using VBS and renamed system tools to hijack PCs via AWS and Tencent Cloud. Stay alert!

Operation DualScript uses parallel execution to bypass defenses, hijacking crypto wallets and banking data via RetroRAT and clipboard swapping.
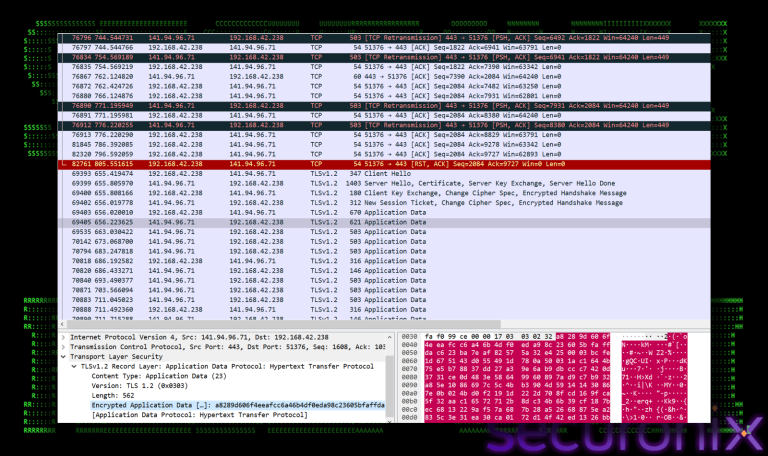
Securonix uncovers FAUX#ELEVATE, a 25-second attack using 10MB "inflated" VBScripts to steal credentials and mine crypto in French corporate environments.

Elastic Security Labs uncovers SILENTCONNECT, a stealthy loader using Cloudflare and Google Drive to deliver RMM tools for "hands-on keyboard" attacks.

BI.ZONE uncovers Forbidden Hyena using AI-generated code to deploy the new BlackReaperRAT and Milkyway ransomware in highly evasive cyberattacks.

Trend Micro exposes KongTuke's new "CrashFix" tactic, which tricks enterprise users via fake Chrome errors into deploying the fileless modeloRAT backdoor.

BlueVoyant uncovers a shift in Mercenary Akula (UAC-0050) tactics, targeting European financial institutions via spoofed judicial lures and RMS malware.

APT28's "Operation MacroMaze" targets Europe using Spanish gov decoys. The campaign uses "low-tech" macros & Webhook.site to evade detection.
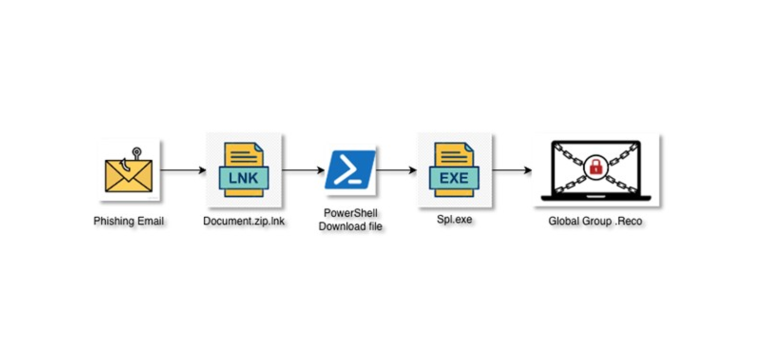
Phorpiex botnet returns in "Your Document" phishing campaign. Attackers use malicious .LNK files and hidden extensions to trick users.

Storm-2603 exploits SmarterMail vulnerability CVE-2026-23760 to deploy Warlock ransomware. Upgrade to Build 9511 immediately to prevent system compromise.
DPRK spies weaponize Visual Studio Code tunnels to bypass security. Darktrace reveals a campaign targeting South Korea with government decoys.

Attackers abuse GitHub, Dropbox, and the "Defendnot" research tool to disable Windows Defender and deploy Amnesia RAT & ransomware in Russia.

Attackers exploit legitimate ahost.exe via DLL sideloading to deploy RATs & stealers. Trusted dev utility bypasses security scanners. Watch out.

Securonix reveals SHADOW#REACTOR: A stealthy framework using "text-only" fragments to deploy Remcos RAT in memory via MSBuild. Avoids disk detection.