 Do Son
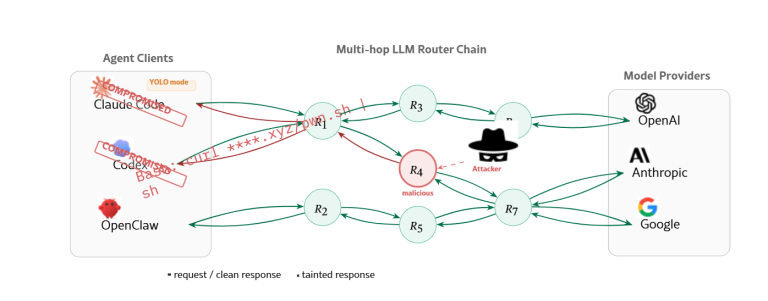
New research reveals massive security gaps in AI API aggregators. From stolen crypto to leaked tokens, learn why your API hub might be a Man-in-the-Middle trap.
LLM infrastructure

Critical CVSS 9.8 flaw in vLLM allows remote code execution via PyNcclPipe. Patch to 0.8.5 now to protect your AI infrastructure.