 Do Son
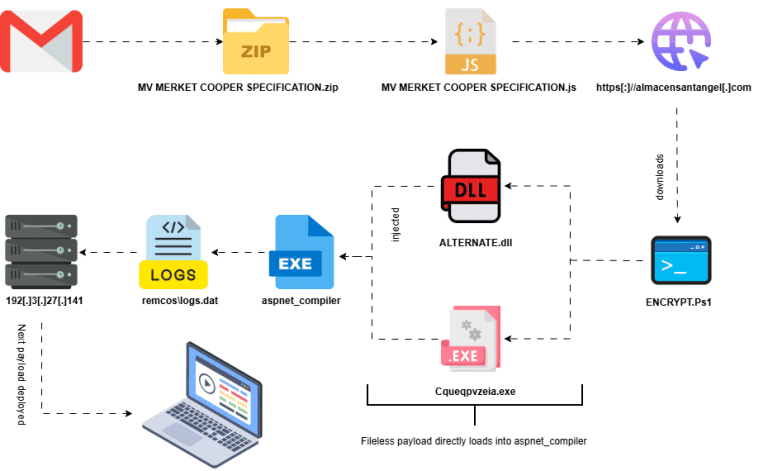
Researchers unmask a fileless Remcos RAT campaign using obfuscated JS and LOLBins to hijack systems in-memory. See the technical breakdown from Lat61.
LOLBins
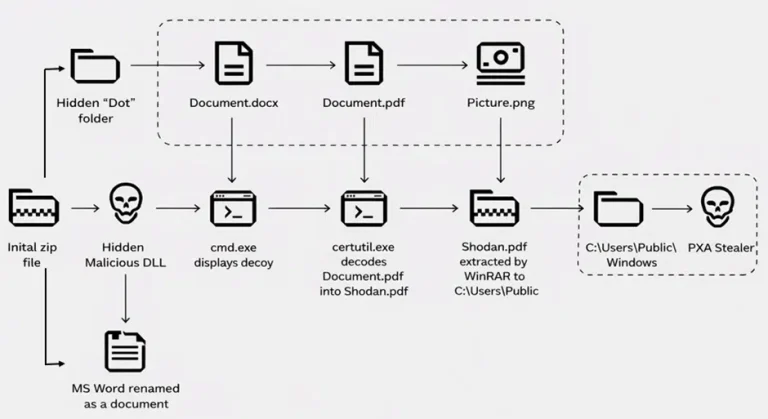
PXA Stealer activity surges in Q1 2026, targeting global finance. Learn how this Python-based malware uses Telegram and LOLBins to hijack crypto and banking data.

Elastic Security Labs uncovers SILENTCONNECT, a stealthy loader using Cloudflare and Google Drive to deliver RMM tools for "hands-on keyboard" attacks.
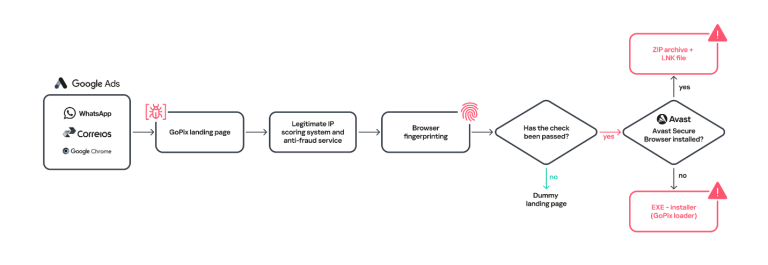
Kaspersky Labs details GoPix, a highly advanced Brazilian banking Trojan using memory-only implants and MitM attacks to target Pix and crypto.
Unit 42 uncovers CL-UNK-1068, a Chinese APT targeting Asian critical infrastructure using stealthy web shells, LOLBINs, and screen-printed exfiltration.

The JS#SMUGGLER campaign uses "Junk Code" JavaScript and fileless PowerShell executed via mshta.exe to bypass EDR. This multi-stage attack silently installs the NetSupport RAT.

Cybereason exposed Tangerine Turkey, a VBScript worm that spreads via USB drives. It uses LOLBins (printui.exe) and Windows Defender exclusions to deploy the XMRig cryptominer for profit.

A new campaign uses a malicious LNK shortcut sent via Discord to deploy a multi-functional RAT that hijacks legitimate Windows binaries to evade detection.

Discover the latest cyber threat: RedCurl APT group. Learn about their sophisticated techniques and targeted cyber espionage campaigns.

Uncover the stealthy techniques threat actors are using: LNK files and SSH commands in advanced cyberattacks.