 Do Son
An Amazon ClickFix campaign uses a fake CAPTCHA and the old Windows finger command to drop Lumma Stealer and NetSupport. Stay protected.
Lumma Stealer
Following the Lumma takedown, the sophisticated AuraStealer malware is rapidly gaining ground, using TikTok scams and stealth to harvest data.
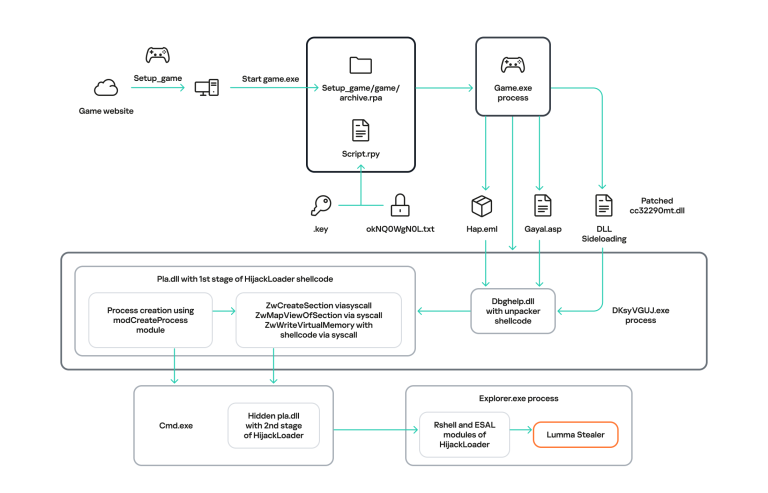
Kaspersky warns: Pirated visual novels are spreading RenEngine malware. Attackers use fake downloads to install ACR Stealer. Protect your data now.

A Lumma Stealer campaign is using fake update lures on Itch.io. The malware uses a Node.js-compiled executable and a reflective loading technique to steal passwords and crypto wallets.

Despite a recent doxxing attempt, Lumma Stealer has resurfaced, integrating browser fingerprinting into its C&C to collect WebGL/Canvas signatures for sandbox evasion and victim assessment.

A new report reveals HijackLoader, a Malware-as-a-Service loader. It uses advanced evasion and anti-analysis techniques to deliver stealers and other payloads.

A new large-scale malware campaign is using GitHub repositories disguised as game cheats and software cracks to distribute SmartLoader and steal user data.

Weeks after a major takedown, Lumma Stealer has resurfaced with new stealth tactics, exploiting cracked software, fake CAPTCHAs, and GitHub to resume its credential-stealing operations.

A malicious campaign on GitHub is distributing Lumma Stealer via fake "Free VPN for PC" and "Minecraft Skin Changer" repositories, using obfuscation and process injection for stealthy delivery.
A sophisticated campaign is exploiting AI tool popularity via Black Hat SEO to poison search results, delivering Vidar, Lumma, and Legion Stealers to unsuspecting users.

Hackers leaked 7.4 million Paraguayan citizen records on the dark web, demanding a $7.4M ransom. The breach likely stems from infostealer malware, sparking national security concerns.

The notorious Genesis Market is back! A new campaign deploys a malicious browser extension via Lumma Stealer to covertly harvest user data.

Global operation neutralizes Lumma Stealer, infecting hundreds of thousands of PCs. Europol & Microsoft seized over 1,300 malicious domains.

Beware! Cybercriminals are using fake CAPTCHA pages to trick you into running commands that install the dangerous Lumma Stealer malware.

Trellix analysis reveals Lumma Stealer's latest tactics: code obfuscation, API hashing, ETW evasion, anti-VM. Learn how this InfoStealer avoids detection.
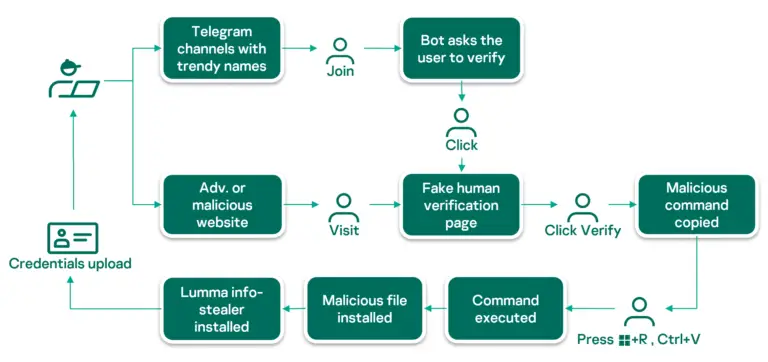
A deep dive into Lumma Stealer's sophisticated techniques: from fake CAPTCHAs to complex infection chains designed to evade detection and steal sensitive data.

Uncover the latest variant of ClearFake malware, EtherHiding, exploiting Web3 features for advanced malicious tactics.

Stay informed about Booking Phishing schemes. Discover how attackers use social engineering to steal credentials in this campaign.

Learn how SmartLoader is being spread through deceptive GitHub repositories, targeting users with gaming and software tools.

The latest report details how malicious actors are leveraging YouTube, Cloudflare, and MediaFire to distribute the Lumma Stealer malware
Discover the new tactics of Angry Likho, a persistent threat group targeting high-profile entities in Russia and Belarus.

Explore the activities of TA2726 and TA2727 as they utilize fake browser updates to spread malware and deceive users.