 Do Son
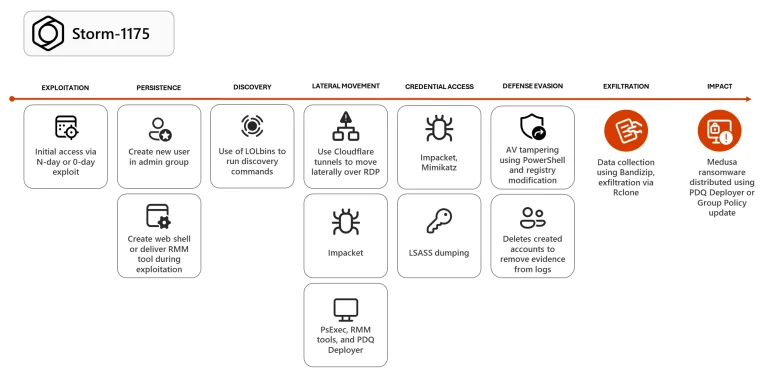
Microsoft exposes Storm-1175: a high-speed threat actor deploying Medusa ransomware in under 24 hours via zero-day exploits. Learn how to stop the blitz.
Medusa Ransomware

Threat hunters expose North Korean state actors using Medusa ransomware to fund global espionage. U.S. healthcare and non-profits are the primary targets.

New Osiris ransomware hits Southeast Asia, linking to Inc & Medusa groups. It uses BYOVD tactics to disable defenses. Unrelated to the 2016 variant.

A Critical (CVSS 10.0) zero-day RCE flaw (CVE-2025-10035) in GoAnywhere MFT is being actively exploited by the Medusa ransomware group, Storm-1175. Patch immediately.

Explore the threat posed by ABYSSWORKER, a driver used to disable EDR systems after being deployed by MEDUSA ransomware.

Explore the rise of Medusa ransomware attacks, increasing by 42%. Understand the threat and protective measures you can take.
Discover how cybercriminals exploited Fortinet FortiClient EMS, exposing critical vulnerabilities and utilizing a sophisticated attack chain.

Discover the unique tactics of the Medusa Ransomware group. From their name-and-shame blog to their multi-platform presence, learn how they operate.

Unit 42 Incident Response Team's investigation into a Medusa ransomware incident has unveiled intricate tactics, tools, and procedures

Over recent weeks, the governmental servers of the Philippines have been severely compromised by an onslaught of cyberattacks