 Do Son
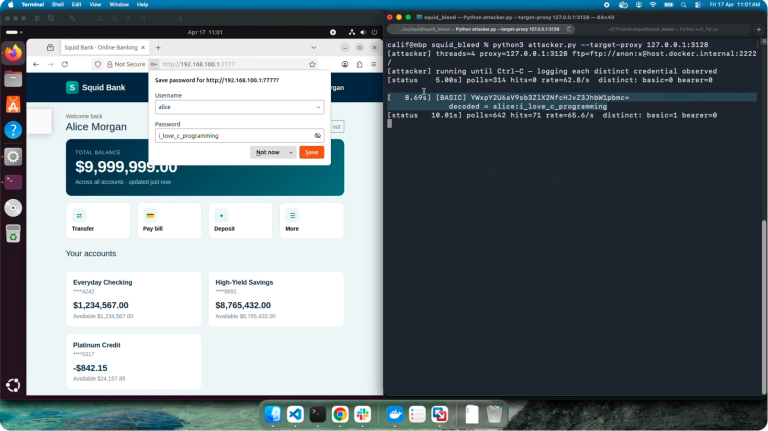
The Squidbleed vulnerability is a Squid proxy memory leak exposing user credentials. CVE-2026-47729 details and PoC exploit code are now public.
Memory Leak

OpenSSL's April 2026 advisory reveals 7 flaws, including a moderate RSA memory leak (CVE-2026-31790). Learn if your version is affected and how to patch.
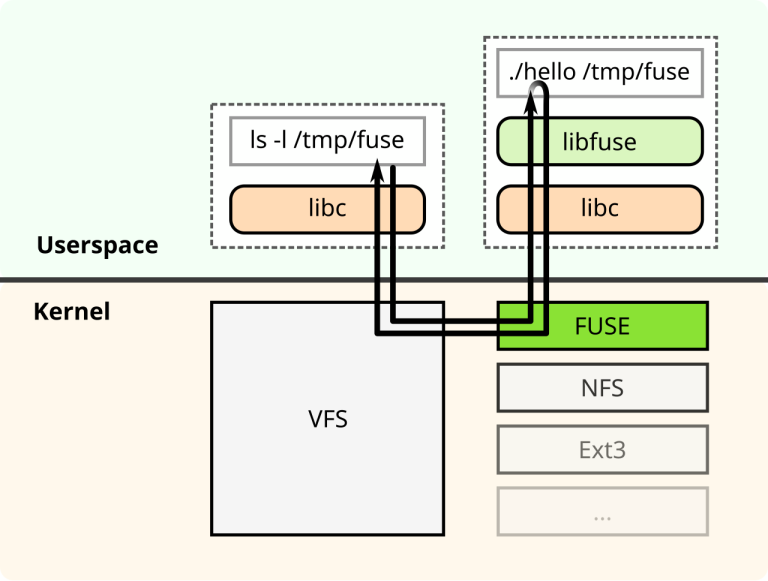
Researchers uncover two flaws in libfuse's io_uring transport (CVE-2026-33150 & 33179). Impacting Kubernetes CSI drivers, these bugs allow RCE and DoS. Patch now!

glibc patches CVE-2026-0861 (CVSS 8.4) & CVE-2026-0915. High-severity heap corruption and a 20-year-old leak affect Linux systems. Patch now.

Urgent: Node.js patches CVE-2025-55131 (High Severity). "Dirty" memory flaw exposes secrets. Update to v20.20.0/v22.22.0 now to stop data leaks.

CISA adds MongoBleed (CVE-2025-14847) to its KEV Catalog after confirming active exploitation. 80,000+ MongoDB servers are at risk. Patch by Jan 19!

MongoBleed (CVE-2025-14847) allows unauthenticated MongoDB memory leaks. With Joe Desimone's PoC released, upgrade to v8.0.17 or v7.0.28 now!

MongoDB CVE-2025-14847: A high-severity flaw in zlib compression allows unauthenticated attackers to read sensitive heap memory. Upgrade to v8.2.3+!

A High-severity flaw (CVE-2025-66566) in lz4-java allows remote attackers to read uninitialized memory (passwords/keys) from recycled buffers during decompression. Update to v1.10.1 immediately.

A PoC has been released for two High-severity flaws in the Linux HID core, allowing malicious USB devices to leak up to 64KB of kernel memory.
DanaBot's "DanaBleed" memory leak, active for 3 years, exposed C2 server data, aiding law enforcement in Operation Endgame takedown.

Two unpatched CVSS 9.8 flaws in telecom gear enable remote code execution via buffer overflows, exposing critical infrastructure to attack.