 Do Son
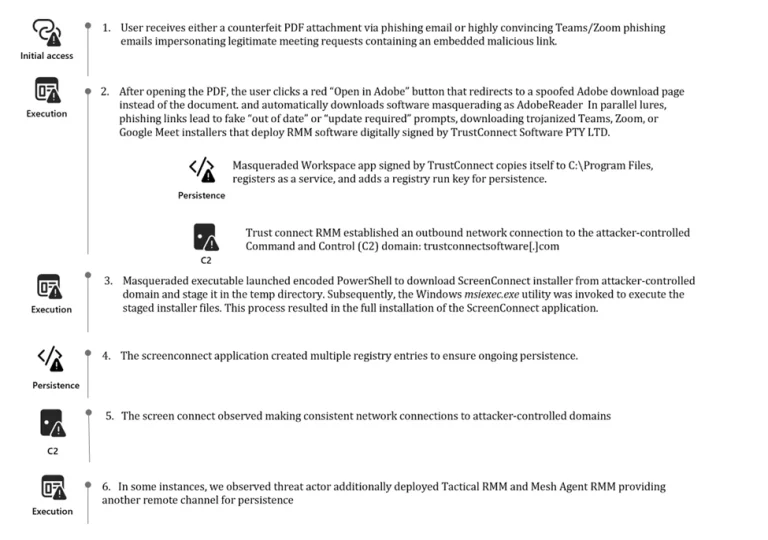
Microsoft Defender exposes a new phishing campaign using EV certificates and fake Teams invites to silently deploy RMM backdoors on corporate networks.
MeshAgent

ASEC uncovers sophisticated attacks targeting South Korean Windows IIS and Linux systems, deploying WogRAT, MeshAgent, and SuperShell for cyber-espionage and lateral movement.

Alert: UAC-0185 (UNC4221) APT group targets Ukraine's defense industry. Discover the tactics behind the phishing campaign and how to protect sensitive systems.

LilacSquid deploys a series of malicious tools, including MeshAgent, a customized version of QuasarRAT, dubbed "PurpleInk,"