 Do Son
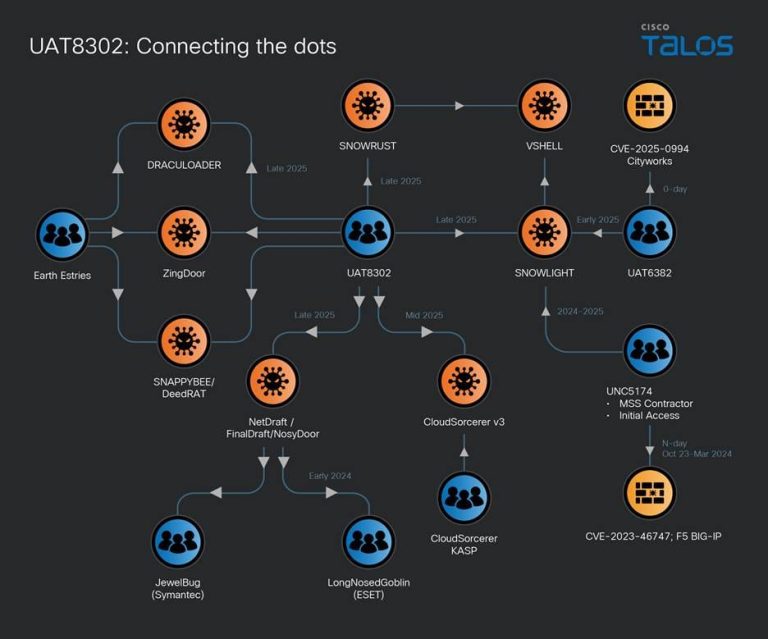
Cisco Talos exposes UAT-8302, a China-linked APT group infiltrating governments via NetDraft and CloudSorcerer. Learn how they share tools with notorious APTs.
Microsoft Graph API

Harvester APT expands to Linux using Microsoft Graph API for C2. Learn how the "GoGra" variant uses Outlook and "Zomato Pizza" lures to evade detection.

Ink Dragon is weaponizing government servers in Europe using a relay-centric mesh. By hijacking IIS servers, they mask C2 traffic across global networks.

Symantec exposed China's Jewelbug APT in an unprecedented 5-month intrusion on a Russian IT provider. The group used Yandex Cloud for data exfiltration and Graph API for stealthy C2 via custom malware.

Explore the latest insights on FUD Malware and how the Havoc framework enables undetectable cyber operations.

Uncover the details of the VEILDrive threat campaign leveraging Microsoft services for C2. Learn how the attackers exploited trusted infrastructure to evade detection.

Microsoft Graph API is being used to facilitate communications with command-and-control (C&C) servers hidden within Microsoft’s cloud infrastructure