 Do Son
A new report reveals that attackers are abusing Microsoft Teams' collaboration features to launch phishing, vishing, and malware attacks, bypassing security warnings.
Microsoft Teams

Matanbuchus 3.0, a new sophisticated malware loader, is using social engineering via Microsoft Teams to infiltrate enterprise systems with advanced evasion tactics.

Zoom's new Custom AI Companion ($12/month) brings agent-like AI to 16 business apps like ServiceNow, Jira, & Asana, offering real-time meeting summaries & task orchestration to boost productivity.

Dylan, 13, became Microsoft's youngest security researcher, uncovering a Teams flaw and prompting a Bug Bounty Program rule change. He has since submitted 20 reports.

The U.S. House of Representatives has banned WhatsApp on government devices, citing security and transparency concerns. Meta strongly disputes the "high-risk" assessment.

Rapid7 reveals BlackSuit ransomware affiliates are adopting Black Basta tactics, using email bombing, fake Quick Assist scams, and evolving Java RATs.

Microsoft Teams is adding a "Prevent Screen Capture" feature that will turn the meeting screen black if someone tries to take a capture. Rolling out July 2025.

New attack campaign uses Microsoft Teams phishing and a novel TypeLib COM hijacking technique for persistence, targeting finance sector.

Learn how Browser Cache Smuggling attack works and how it can exploit browser behavior to deliver malicious payloads undetected.

Learn about QBACKCONNECT and its role in the tactics of Black Basta and Cactus ransomware groups for cyber threats.

Explore the changes in Skype paid services and how they affect new users and existing subscribers after the transition.

NVISO Labs uncovers a new phishing campaign by Black Basta. See how they employ Microsoft Teams as a tool for social engineering attacks.
Black Basta Ransomware Group Elevates Social Engineering with Microsoft Teams and Malicious QR Codes

Black Basta Ransomware Group Elevates Social Engineering with Microsoft Teams and Malicious QR Codes
Uncover the latest tactics of the Black Basta ransomware group targeting diverse sectors and geographies. Stay informed about the intensified social engineering campaign.

Rapid7, a cybersecurity firm, has uncovered a recent malvertising campaign using fake software installers to distribute the Oyster backdoor

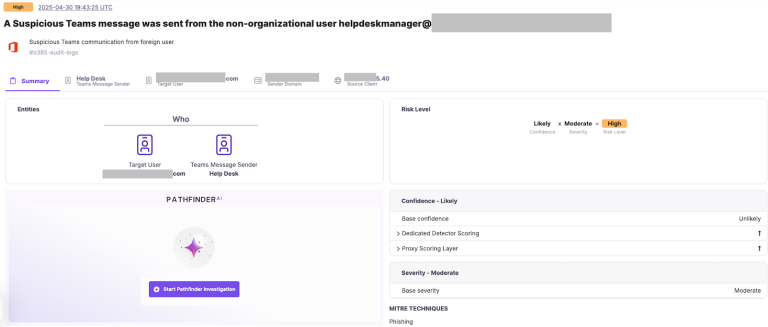
The MDR team’s subsequent investigation uncovered over 1,000 “MessageSent” Teams events linked to the external user
At present, Ubisoft is reluctant to disclose detailed information about this data breach. Several days have elapsed since the incident