 Do Son
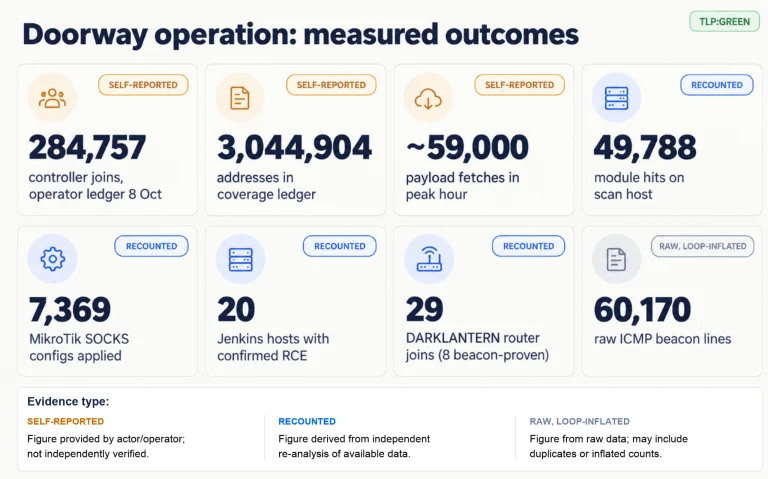
CloudSEK uncovers the Doorway botnet. The Rust Doorway botnet exploits routers, cameras, and servers to build a global proxy network.
MikroTik
A critical MikroTik RouterOS vulnerability, CVE-2026-84411 (CVSS 9.8), lets unauthenticated attackers run code as root. Update RouterOS now.
The MikroTrick PoC is publicly disclosed. This MikroTrick RouterOS flaw is actively exploited in the wild, granting full administrative privileges.
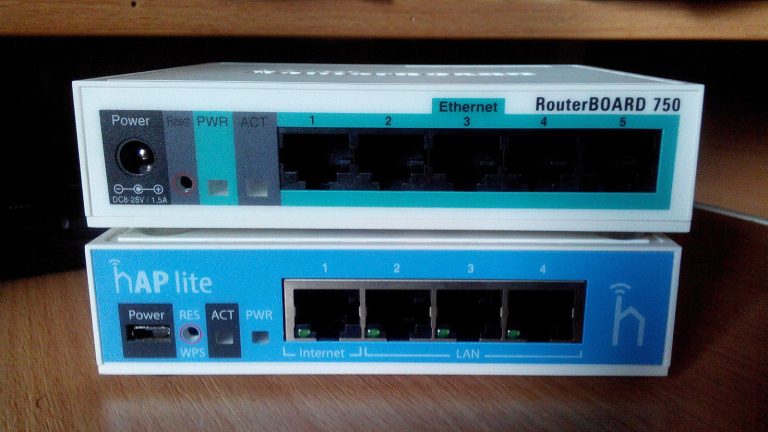
A critical MikroTik RouterOS vulnerability is actively exploited in the wild. Learn how to detect rogue ops accounts and apply the latest firmware updates.
CVE-2026-16347 lets attackers brute-force MikroTik RouterOS logins for unauthorized system access. Rated CVSS 8.8, with no fix yet. Apply mitigations.
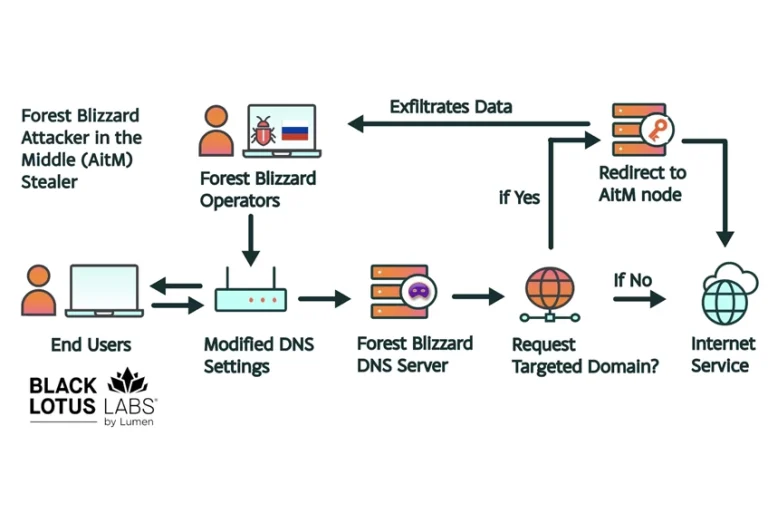
Russian-linked Forest Blizzard's FrostArmada campaign hijacked 18,000+ routers to steal OAuth tokens via DNS redirection. Learn how they stayed invisible.

NCSC unmasks APT28’s "digital funnel" using router DNS hijacking to steal OAuth tokens and passwords. Protect your remote workforce—patch your routers now.

A Critical (CVSS 10.0) flaw (CVE-2025-61481) in MikroTik RouterOS/SwOS exposes the WebFig management interface over unencrypted HTTP by default, allowing remote credential theft via MitM.

Uncover the dangers of DNS misconfiguration and its role in a massive botnet operation. Learn how hackers exploit SPF records to distribute malware.