 Do Son
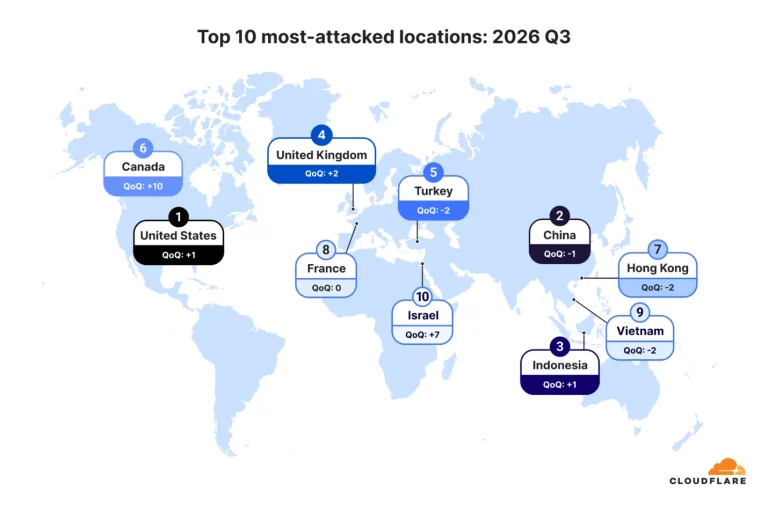
The Cloudflare DDoS report Q3 2026 reveals 18.2M network attacks, a 208% surge in short-burst floods, and a major shift toward DNS and UDP attacks.
Mirai botnet
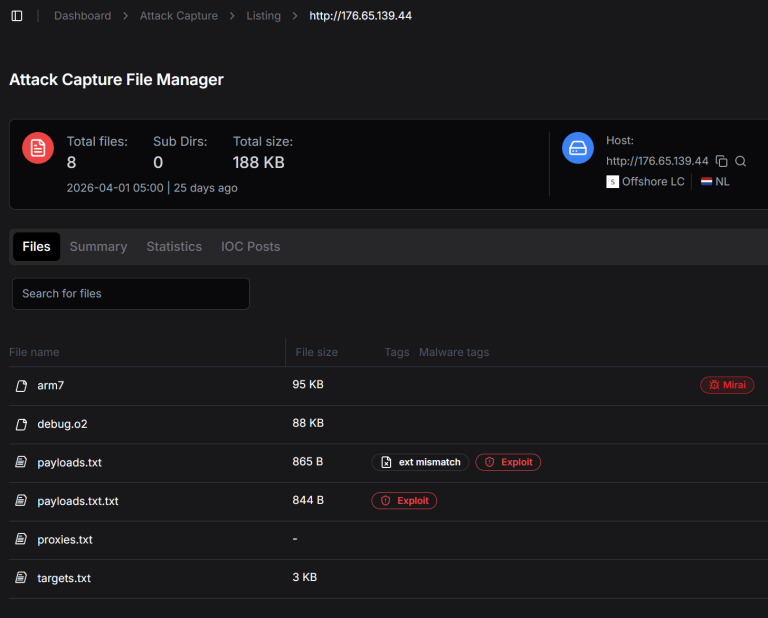
Hunt Intelligence dismantles xlabs_v1, a Mirai-derived botnet targeting 4M Android devices via port 5555. See how an exposed server leaked the entire toolkit.
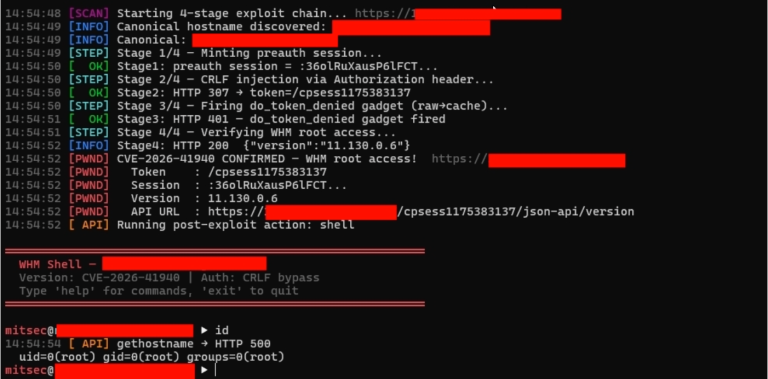
CISA warns of cPanel CVE-2026-41940 (CVSS 9.8). 44,000 IPs compromised via authentication bypass, fueling ransomware and botnets. Patch by May 3rd!

Akamai SIRT warns of a new Mirai campaign weaponizing EOL D-Link routers via CVE-2025-29635. Protect your network from zombie botnets—retire old hardware now.
Akamai SIRT reveals Zerobotv9, a new Mirai-based botnet targeting enterprise n8n workflow platforms and Tenda routers via critical vulnerabilities.

Stan Ghouls group targets Uzbekistan via fake court emails and malicious Java loaders. Learn how they deploy NetSupport RAT to spy on victims.

FortiGuard exposed ShadowV2, a new Mirai botnet variant that launched an IoT test attack specifically during a global AWS outage. The XOR-encoded malware targets routers and uses a hardcoded fallback C2 for resilience.

Zyxel firewalls are under a coordinated attack exploiting critical RCE flaw CVE-2023-28771 (CVSS 9.8) via UDP port 500, likely by Mirai botnets. Patch immediately

Stay informed about the security risks of TVT NVMS9000. Learn about a major vulnerability that exposes DVRs to cyber attacks.

Explore the rise of Mirai malware exploiting IoT vulnerabilities in Edimax devices and find out how to protect yourself.

Learn about a record-breaking DDoS attack that targeted an internet service provider in East Asia. Discover how Cloudflare's advanced defense system neutralized the threat.

Discover the resurgence of the XorBot botnet, a potent threat to IoT devices worldwide. Learn about its advanced anti-detection mechanisms and wide range of exploits.

Discover the alarming implications of CVE-2024-7029, a zero-day vulnerability in AVTECH IP cameras exploited by the Corona Mirai botnet campaign.
Learn about CVE-2024-45163, a critical vulnerability in the Mirai botnet. Discover how this flaw can be exploited for remote DoS attacks.

The active exploitation of CVE-2024-29973 by a Mirai-like botnet underscores the urgency of applying the necessary security patches

Attackers are weaponizing two critical vulnerabilities, CVE-2023-46805 and CVE-2024-21887, to spread the notorious Mirai botnet malware
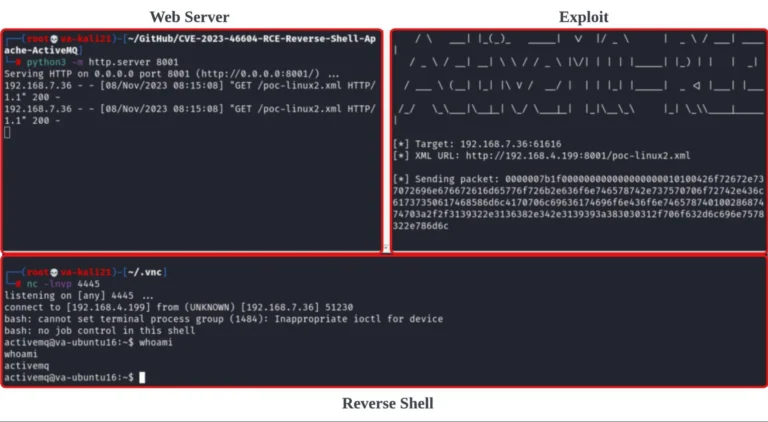
Cybereason Security Services has sounded the alarm about a dangerous wave of attacks targeting a critical vulnerability in the Apache ActiveMQ

Security researchers from xlab-qianxin detected Mirai.TBOT, a variant of the original Mirai, operates with distinct characteristics

This vulnerability cataloged as CVE-2023-49897 with a CVSS v3 score of 8.0, allows authenticated attackers to execute OS commands remotely

Utilizing several vulnerabilities, IZ1H9 poses a serious threat, taking full control of compromised devices to form part of its botnet.

The swift exploitation of CVE-2023-1389 by the Mirai botnet underscores the decreasing "time-to-exploit" speed observed
Since the source code for the Mirai botnet was released in 2016, FortiGuard Labs has discovered a...