 Do Son
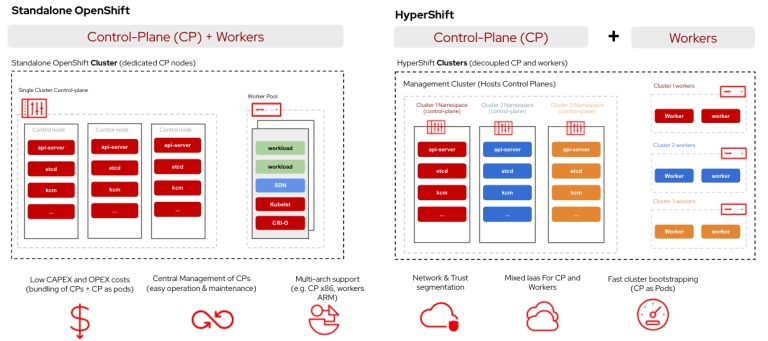
A Konnectivity vulnerability (CVE-2026-16242, CVSS 9.4) lets unauthenticated attackers proxy and modify control-plane traffic. See the fix and mitigation.
mitm
Apache Thrift fixes critical cross-language vulnerabilities (MitM, memory corruption, DoS). Secure your Java, Go, and C++ stacks by upgrading to version 0.23.0.

Synology patches critical DSM flaws (CVSS 8.0) allowing file manipulation and data leaks. Secure your NAS—upgrade to DSM 7.3, 7.2.2, or 7.2.1 immediately!

F5 warns of NGINX flaw CVE-2026-1642 (CVSS 8.2). MITM attackers can inject data into upstream TLS responses. Update to v1.29.5 immediately.

ConnectWise patched two high-severity flaws in Automate RMM. CVE-2025-11492 (CVSS 9.6) allows MiTM attack to intercept unencrypted agent communications and inject malicious updates. Update to 2025.9.

A medium-severity vulnerability (CVE-2025-9708) in the Kubernetes C# client allows MITM attacks and API impersonation. Update now to patch.

The Opossum Attack is a new desynchronization flaw exploiting implicit/opportunistic TLS in protocols like HTTP, allowing MitM to compromise encrypted connections. Over 3M servers affected.

Hitachi Energy warns of 5 flaws in MicroSCADA X SYS600 (v10.0-10.6), including remote DoS, data leaks, and TLS MITM, risking power system control.

A flaw (CVE-2025-49146) in PostgreSQL JDBC Driver allows MITM attacks even with channel binding enabled. Upgrade to v42.7.7 or use sslMode=verify-full.

bettercap kali linux,bettercap mitm,bettercap tutotrial,ettercap sslstrip