
 Do Son
Iranian group Seedworm infiltrates global firms using automated Node.js scripts and DLL sideloading via trusted binaries. Protect your credentials now!
MuddyWater

Rapid7 unmasks Iranian APT MuddyWater using a Chaos ransomware "false flag" to hide state-sponsored espionage. See how they bypassed MFA via MS Teams.
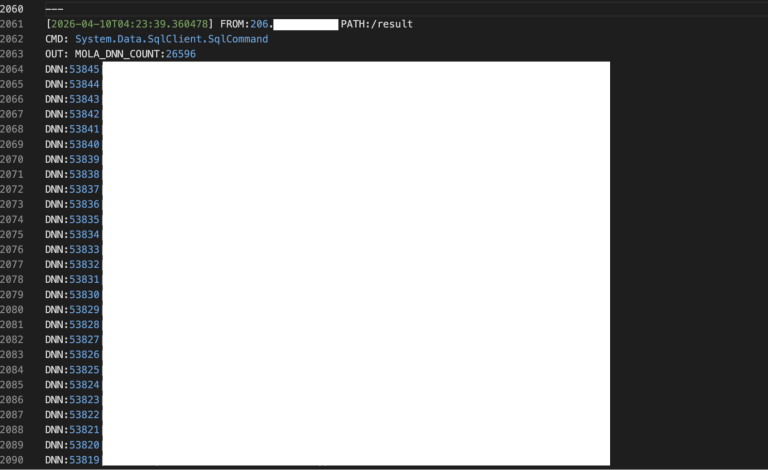
Hunt Intelligence uncovers a massive Iranian-nexus breach targeting the Omani Ministry of Justice. 26k records leaked via an unprotected UAE staging server.
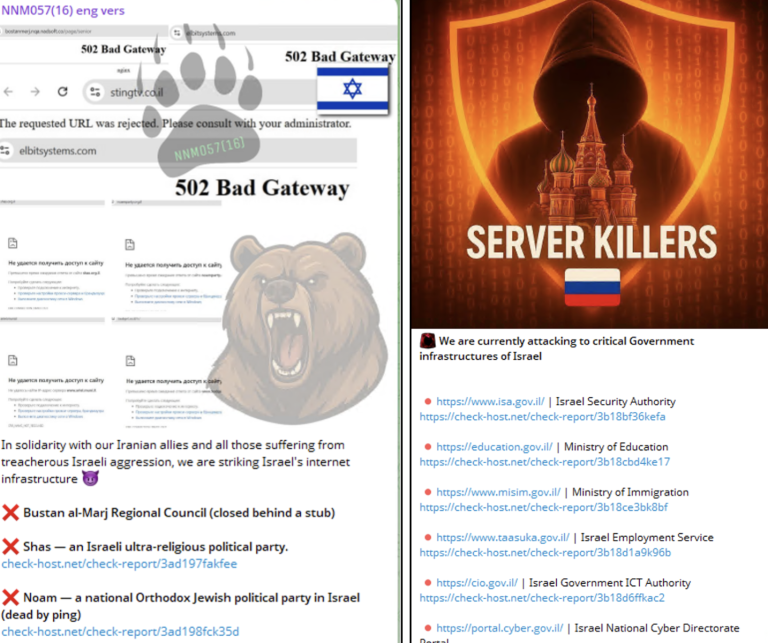
Rapid7 reveals a surge in state-directed cyber espionage and noisy hacktivism. Learn how actors like MuddyWater exploit critical CVEs to breach networks.

Iranian APT Seedworm intensifies cyberespionage against US and Israeli networks using a new stealth backdoor called Dindoor. Read the full threat report.

MuddyWater APT deploys new "RustyWater" malware against Middle East targets. CloudSEK reveals how the group is ditching PowerShell for stealthy Rust tools.
FortiGuard exposed UDPGangster, a custom UDP backdoor deployed by MuddyWater APT. The malware evades network defenses and analysis by using UDP for C2 and checking for single-core CPUs/low RAM.

Group-IB exposed MuddyWater using NordVPN to send phishing emails that deliver the Phoenix v4 backdoor. The malware steals credentials via a custom Chromium stealer disguised as a calculator.
Group-IB reports on MuddyWater, an Iranian APT, shifting tactics from RMM tools to custom malware and spearphishing, using new backdoors like Phoenix.

A new report reveals a sophisticated spear-phishing campaign targeting finance executives. The attack uses social engineering and legitimate tools to evade detection.

A targeted phishing campaign against Israeli organizations uses a PowerShell-based RAT and compromised internal emails for delivery, making detection difficult.

Lookout uncovers an evolved DCHSpy Android spyware linked to Iran's MuddyWater APT, targeting high-value geopolitical entities with new Starlink and VPN lures.

Discover the alarming tactics of the MuddyWater hacking group. Find out how they exploit legitimate software in their attacks.

MuddyWater, an Iranian state-backed hacking group, is exploiting the legitimate remote monitoring and management (RMM) solution

A sophisticated campaign spearheaded by MuddyWater, an entity known for its state-sponsored activities, unveiling the DarkBeatC2 framework

the Iranian espionage group Seedworm (also known as Muddywater) has emerged as a sophisticated and elusive adversary

In the wake of these findings, Deep Instinct has unearthed additional suspected MuddyC2Go servers at Stark Industries