 Do Son
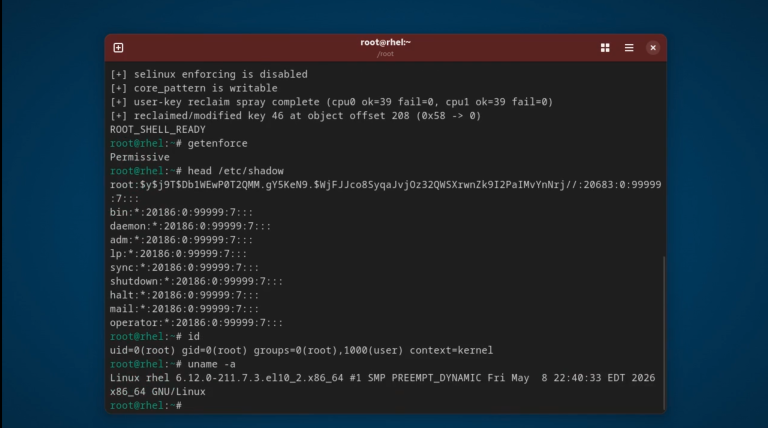
CVE-2026-74480 (CVSS 9.8) enables Linux kernel privilege escalation via a bridge use-after-free. Exploit code and a demo are now public.
Nebula Security
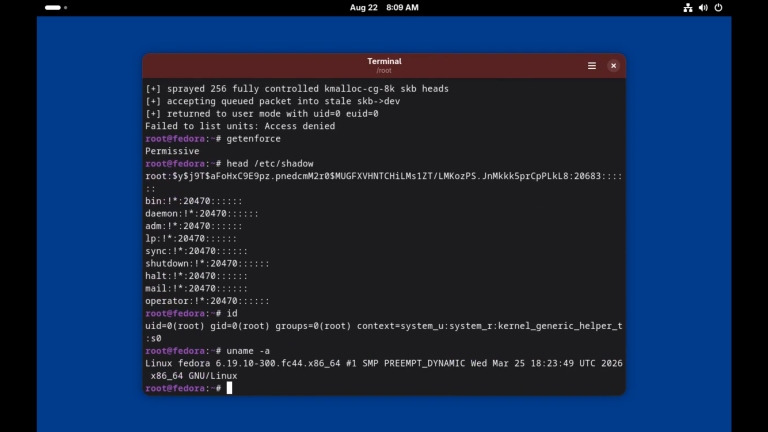
CVE-2026-52912, a Linux kernel netfilter use-after-free, now has public PoC exploit code enabling root privilege escalation.

Urgent: Millions affected by "nginx-poolslip," a critical Nginx 1.31.0 zero-day that bypasses ASLR via heap feng shui to grant unauthenticated remote RCE.